I will build and tune splunk siem detection rules and correlation searches

Saudi Arabia

I speak English, Arabic

Cyber Security Defense Expert

I am a Cyber Security Defense Expert with seven years of experience in managed security services across Saudi Arabia's regulated sectors. I specialize in threat-informed defense, detection engineering...
About this Gig

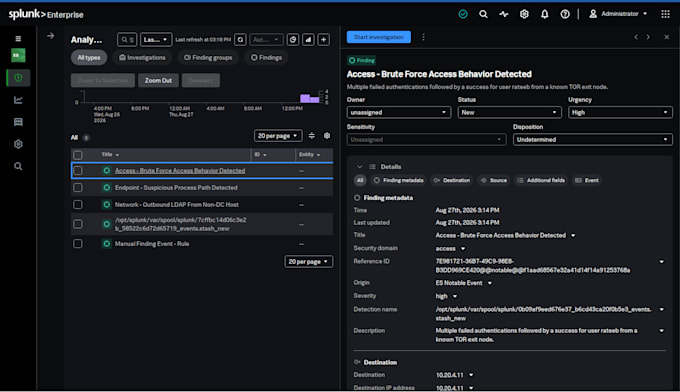
I build Splunk detection content that fires on real attacker behaviour and stays quiet otherwise.

Seven years in security operations, most of it in detection engineering. I have written and tuned correlation searches across enterprise Splunk ES environments and mapped over 274 rules to MITRE ATT&CK.

What you get

  • Working SPL tested logic, not pseudocode
  • Rules mapped to MITRE ATT&CK techniques
  • Tuning so your analysts are not drowning in false positives
  • Documentation: what each rule detects, which data sources it needs, what a true positive looks like

Common requests I handle

  • New detections for a specific threat or technique
  • Fixing noisy rules that analysts have started ignoring
  • Coverage gap analysis against MITRE ATT&CK
  • CIM field mapping and data source validation

To get started I need

Your Splunk version, the indexes and sourcetypes in scope, which data sources are onboarded, and sanitised sample events. No production logs, no real IPs or hostnames.

Not sure what you need? Message me first and I will tell you honestly whether I can help.
Related tags