Browse categories
English
$
USD
Connect to your AI
Network Cloud Security Engineer, SOC Engineer, Ethical Hacker
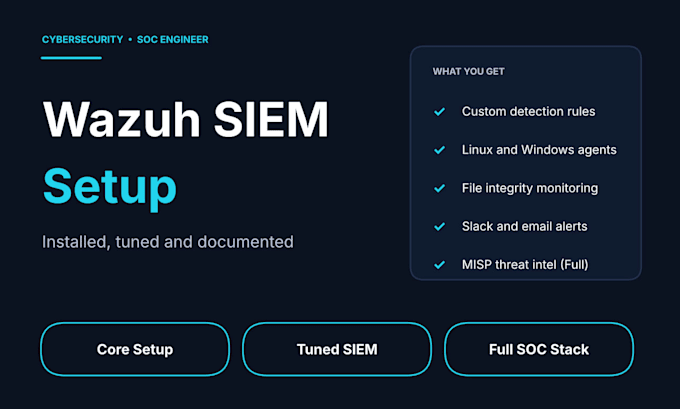
Need a SIEM that actually produces useful alerts? I design and run production SOCs for a living, and I'll deploy Wazuh for you the right way: configured, tuned and documented.
WHAT YOU GET
WHAT I NEED FROM YOU
A Linux server (Ubuntu or similar), remote access, and a list of the systems you want monitored.
HOW IT WORKS
Message me before ordering with your environment and goals. Ill confirm the right package, then deliver on schedule with documentation.
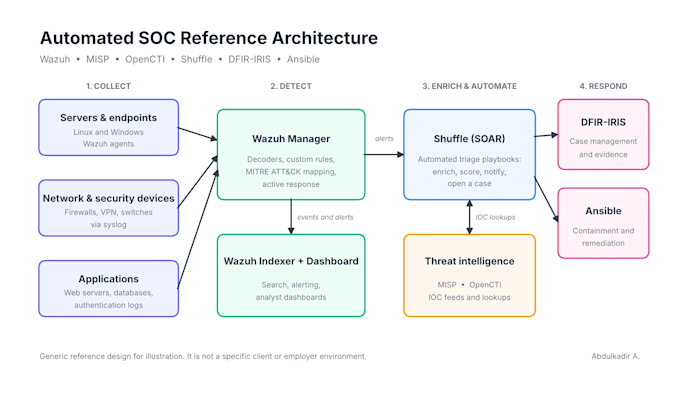
Full SOC Stack adds firewall log integration, MISP threat intelligence, and automated response.
Server:
Virtual private server
•
Windows server
•
Other
Operating system:
Windows
•
Linux
Which systems do you support?
Ubuntu, Debian and RHEL-based Linux servers, with agents for Linux and Windows machines.
Do you need access to my systems?
Only to the Wazuh server and the machines getting agents, through temporary access you can revoke afterward. Never send passwords in chat.
Is this ongoing monitoring?
No, this gig is setup and handover. Message me if you need ongoing support.