Browse categories
English
$
USD
Connect to your AI
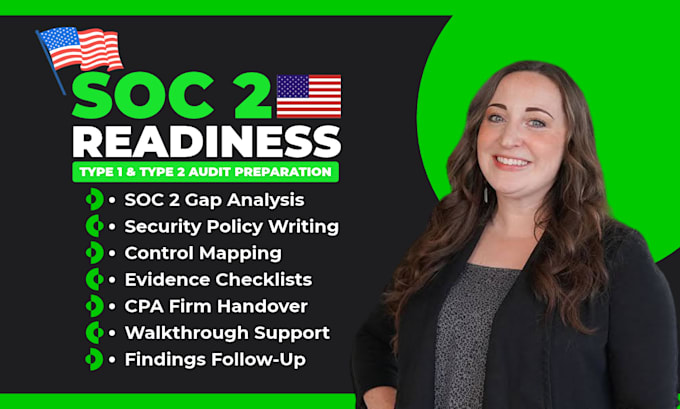
Has a customer asked for your SOC 2 report, but your policies and evidence are scattered across teams?
I've helped B2B and technical teams turn complex information into clear documentation. I bring that experience to SOC 2 Type 1 and Type 2 readiness for SaaS companies, software vendors, and IT service providers.
Depending on your package, I can help with:
I'll show you which records support your controls, where evidence is missing, and what your team needs to do next. With audit coordination, I can join agreed walkthroughs as your consultant and help your team respond to findings. The independent CPA firm conducts the examination and issues the SOC 2 report under a separate engagement.
Message me with your target date and whether you already have a CPA firm.
SOC 1 and SOC 2 Readiness with ISO 27001 Documentation
Languages
What does a SOC 2 readiness gap analysis include?
I review the agreed policies, control documentation, and available evidence for one system. You’ll get written findings that explain what your team can demonstrate, where documentation or evidence is missing, and which gaps to address first.
Can you help with SOC 2 Type 1 and Type 2 audit preparation?
Yes. For Type 1, I help organise documentation and evidence for the agreed date. For Type 2, I help map controls to the records your team needs to retain throughout the examination period.
Can you write SOC 2 security policies for a SaaS company?
Yes. I tailor agreed policies to how your team works. Common topics include access management, employee offboarding, and incident response. Your team reviews and approves each draft.
Can you help me find a CPA firm and attend the SOC 2 audit?
Yes. I can help you identify an independent CPA firm and organise the handover. With your approval and the firm’s agreement, I can join walkthroughs, explain the documentation I prepared, and track follow-up requests. Your team handles firsthand questions and formal sign-off.
Does the package include the final SOC 2 report?
The package covers the readiness or coordination deliverables listed. You engage the independent CPA firm directly for the examination and SOC 2 report. The firm sets its own fee and timeline.
