Browse categories
Explore
Fiverr Pro
English
$
USD
Cloud Security Architect and Compliance Lead
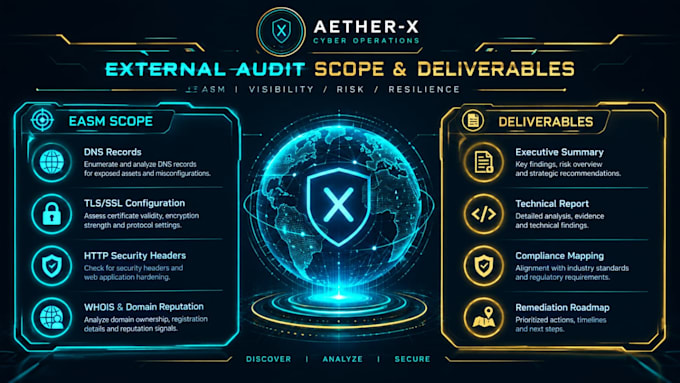
External Attack Surface (EASM) Audit DNS, TLS & HTTP Security Review
Your AWS console can be perfectly locked down and you can still be exposed through your public DNS records, an outdated TLS configuration, or missing HTTP security headers.
WHAT YOU GET:
External Perimeter Executive Summary
DNS, TLS, and HTTP Header Vulnerability Report
WHOIS & Domain Reputation Analysis
Actionable Remediation Roadmap (exact records & headers to configure)
WHY CHOOSE THIS SERVICE?
100% Passive: Nothing is sent to your servers beyond standard public queries.
No AWS Access Required: Purely external, perimeter-level analysis.
Copy-Paste Fixes: Every finding comes with a ready-to-use fix.
HOW IT WORKS & DELIVERY:
Not sure if your domain is leaking information it shouldn't be? Let's find out.


Cloud provider:
Amazon Web Services
Expertise:
Configuration
•
Other
Cloud computing resource:
ELB
•
Route53
•
VPC
•
Security Groups
•
DNS
Do you need access to my servers or AWS account?
A: No, this is a purely external, passive assessment. We only analyze your public-facing domain and records.
Will this scan affect my website performance?
A: No, all checks are passive and non-intrusive. Your website and live environment remain untouched.
What do I need to provide to get started?
A: Your public domain name(s) and the details of the person authorizing this assessment. I will provide a Rules of Engagement (RoE) document to sign.
Can you help fix the issues found?
A: As an external auditor, we cannot modify your live DNS/TLS/web-server settings. We provide a detailed Remediation Roadmap with exact fixes for your team. The Premium tier includes a Re-verification Scan to confirm success.
How long does it take to receive the report?
A: Basic: 2 days, Standard: 3 days, Premium: 5 days.