Browse categories
Explore
Fiverr Pro
English
$
USD
AWS and Terraform Engineer, AI Voice Agents, Full Stack Developer
Level 2
Has met high performance criteria and has a proven track record for meeting client expectations.
Tired of clicking around the AWS console and hoping your setup is secure? With 4 years of hands-on AWS experience, I will build your infrastructure as clean, reusable Terraform code with security built in from day one.
What I build with Terraform:
Security included:
You get: modular, commented code, a README with deploy steps and an architecture diagram.
I can also import existing AWS resources into Terraform or fix and refactor your current code.
Message me before ordering so I can review your requirements and suggest the right package.

Tools:
Docker
•
GitLab
•
GitHub
•
Cloud Formation
•
Hashicorp Vault
Framework:
Terraform
Cloud Provider:
Amazon Web Services
Programming language:
Bash
•
Python
Expertise:
Migration
•
Development
•
Configuration
What do you need from me to get started?
Your project goals, which AWS services you need, the AWS region, and IAM access (or I can deliver code for your team to apply). I will review everything and confirm the scope before I start.
Do I need to share my AWS root account?
No. I only need an IAM user or role with the required permissions. I never ask for root credentials and recommend you remove my access after delivery.
Can you import my existing AWS infrastructure into Terraform?
Yes. I can import resources you created manually in the console into Terraform, so you can manage everything as code going forward.
Can you fix or refactor my existing Terraform code?
Yes. I can debug errors, clean up messy code, split it into reusable modules and set up proper remote state.
How do you make the infrastructure secure?
I follow AWS best practices: private subnets, least-privilege IAM, encryption with KMS, logging with CloudTrail, threat detection with GuardDuty and CIS aligned settings. Every delivery is scanned with Checkov or tfsec.
Do you support multiple environments?
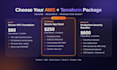
Yes. The Premium package includes separate dev, staging and production environments using reusable modules and variables.
Will you set up CI/CD for Terraform?
Yes. I can set up GitHub Actions or GitLab CI to run terraform plan, security scans and apply with approval.
What happens after delivery?
You get the full source code, a README with deploy steps and an architecture diagram. I will answer questions about the delivery and help with small follow-up fixes.


