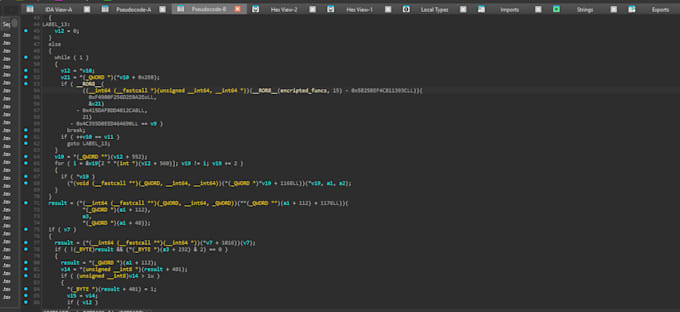
I will reverse engineer windows executables, dlls and drivers for you

A
agarald
A
agarald
Agarald

About this gig

Do you have a Windows binary without source code and need to understand what it does, how it works, or if it contains vulnerabilities? I perform static and dynamic analysis of executables, DLLs, services, and drivers, delivering a clear technical report with findings, execution flow, and recommendations.

My specialty is analyzing native Windows components: kernel-mode drivers, privileged services, obfuscated or packed code. I work regularly with IDA Pro, Ghidra, WinDbg, and x64dbg.

What the service includes:

  • Static analysis: Disassembly, control flow analysis, critical function identification, string and constant search, data structure reconstruction.
  • Dynamic analysis: Controlled execution in an isolated environment, system call monitoring, file and registry access, network traffic, process and thread creation.
  • Deobfuscation & unpacking: Analysis of binaries protected with commercial or custom packers, bypassing anti-debugging and anti-VM.
  • Exploitability assessment: If a vulnerability is identified, I evaluate whether it's practically exploitable and under what conditions.
  • Technical report: PDF document with findings, evidence (screenshots, logs, code snippets)

Get to know Agarald

Agarald
  • FromSpain
  • Member sinceOct 2025
  • Avg. response time1 hour
  • Languages

    English, Spanish
Windows internals & C++ systems engineer. Expert in C++23/20/17: custom PE loaders, parsers, bytecode VMs, IPC. Kernel-mode: WDM drivers, WinAPI, IOCTLs, memory/paging. Reverse engineering with IDA, x64dbg, WinDbg; malware analysis, hooking, evasion. Red team tooling: shellcode, process hollowing, manual mapping, ROP. Blue team: Sentinel, Defender, SentinelOne triage, log correlation. Rust, Python, Linux/Windows admin, CI/CD, networking.

Other Software Development Services I Offer