Browse categories
English
$
USD
Connect to your AI
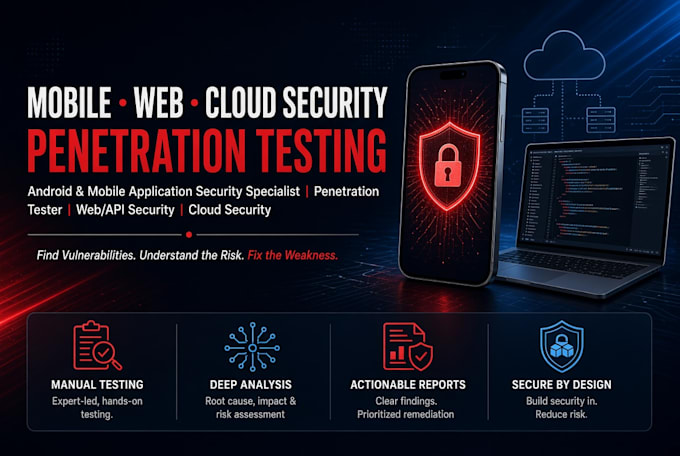
I will perform an authorized security assessment and penetration test of your mobile, web, API, or cloud environment.
My focus is identifying real security weaknesses, validating findings, assessing their potential impact, and providing practical remediation guidancenot simply generating automated scanner results.
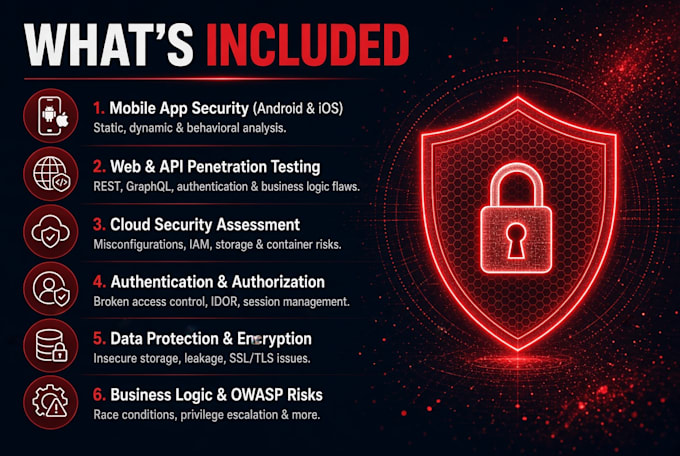
My expertise spans Android & mobile application security, web application security, REST/GraphQL API security, vulnerability assessment, and cloud security. My Android/mobile specialization includes APK analysis, static and dynamic testing, authentication and authorization testing, insecure data-storage assessment, application security controls, and mobile security risks. I also perform OWASP-focused web testing, API security testing, and cloud security configuration/hardening assessments.
Depending on the selected package and agreed scope, you will receive a structured security report containing validated findings, severity, affected components, evidence, security impact, and actionable remediation recommendations.
All testing is performed only against systems and applications for which the client has authorization.
Age range:
Youth
Education:
Highschool education
Device:
Linux
•
iPhone
•
Android mobile phone
•
Android tablet
Language:
Arabic
•
English
•
Nigerian
What can you assess?
I can assess authorized Android/mobile applications, web applications, REST/GraphQL APIs, and selected cloud environments. The exact scope depends on the package and agreed assessment objectives.
Do you perform manual penetration testing?
Yes. Automated tools may support the assessment, but findings are investigated and validated rather than relying solely on automated scan results.
Can you test both an application and its API?
Yes. An Android/mobile application and its supporting API can be assessed together when included in the selected package and authorized scope.
What will I receive after the assessment?
You will receive a structured security report covering identified findings, severity, affected components, evidence, potential impact, and recommended remediation.
Can you retest vulnerabilities after we fix them?
Yes. Remediation retesting can be included where specified in the selected package or purchased as an additional service.