Browse categories
English
$
USD
Connect to your AI

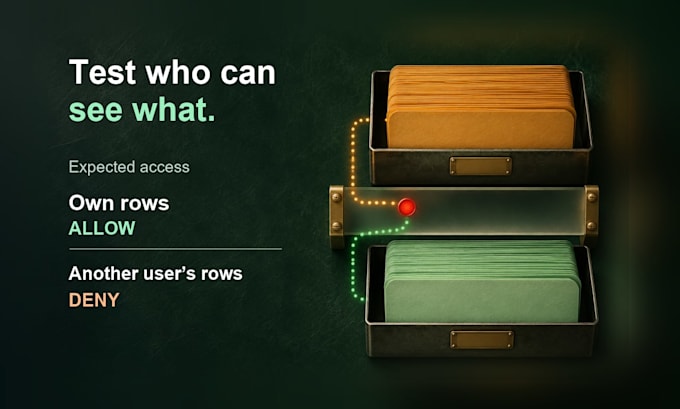
Can one of your users see another user's data? Can they make themselves an admin or switch on your paid plan? I check that for Supabase apps by actually trying it.
You only send your schema. No keys, no project access, no user data. I load it into a throwaway Postgres, create test users and try every read and write as a logged-out visitor and as a logged-in user going after someone else's rows.
You get a table-by-table list of what's open and what's blocked, with the problems ranked in plain language. With Test and fix you also get a SQL fix, and I rerun the same tests so you can see it passes and your users can still reach their own data.
Good for Lovable, Bolt, Cursor or hand-built apps about to launch, or when a customer starts asking about security.
This isn't a pen test or a compliance certificate, and it doesn't cover Edge Functions or app code. You apply the fix yourself, on staging first.
Message me before ordering with your table count and I'll tell you which package fits. There's a sample report in the gallery.
QA tester and English Romanian translator
Languages
Do you need my service key?
No, and please don't send it. The schema is all I need.
How do I get the schema?
Run supabase db dump with the Supabase CLI, schema only, no data. If that's not possible, message me first and we'll find another way.
What if nothing is wrong?
You still get the report showing what was tested and passed. If you ordered Test and fix and there's nothing to fix, you only pay for the RLS test.
Does this make my app secure?
It shows how your database permissions really behave. It doesn't cover app code, Edge Functions or Auth settings, so a clean result isn't a full security guarantee.