Browse categories
Explore
Fiverr Pro
English
$
USD
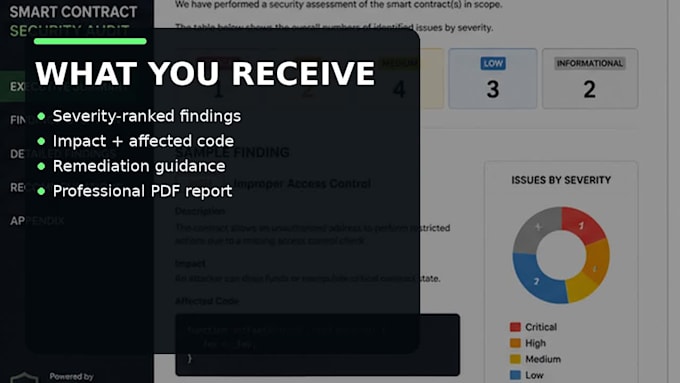
I will perform a professional security audit of your Solidity and rust smart contracts to identify vulnerabilities, logic flaws, access-control issues, and risky implementation patterns. You will receive a clear, severity-ranked audit report with actionable recommendations to help secure your EVM, DeFi, token, NFT, staking, or Web3 project before deployment.


Tools:
MythX
•
Slither
•
Truffle
Cryptocurrency services focus solely on developing and programming. Never share sensitive information or private keys with others.
What do you need to start?
Smart contract source code or repository, Solidity/compiler version, project documentation, deployment target/network, and a short explanation of the intended behavior.
What vulnerabilities do you check for?
I review access control, reentrancy, authorization issues, logic errors, unsafe external calls, arithmetic/economic issues, front-running concerns, initialization problems and other Solidity/EVM security risks relevant to the project.
Will I receive an audit report?
Yes. You will receive a structured PDF report containing findings, severity, impact and recommended remediation.
Do you audit DeFi protocols?
Yes, depending on complexity. Please contact me before ordering for lending, AMMs, vaults, staking, oracle-dependent systems or multi-contract protocols.
Can you check my fixes afterward?
Yes. Standard and Premium can include a recheck after remediation.
Does an audit guarantee my contract cannot be hacked?
No. A security audit significantly improves assurance and identifies known risks, but no professional audit can guarantee that software contains zero vulnerabilities.