Browse categories
English
$
USD
Connect to your AI
Alex T. was selected by the Fiverr Pro team for their expertise.
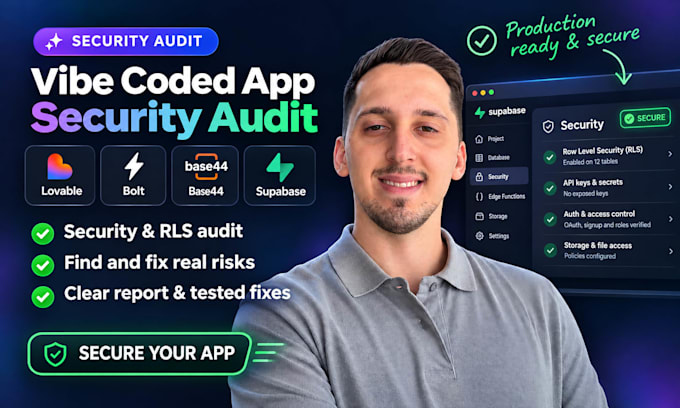
Built your app with Lovable, Bolt, Base44, Replit or Cursor, and now real users are signing up? An August 2026 scan found that 57% of reachable Supabase-backed vibe coded apps let anyone read database tables without logging in.
I'm a senior full-stack and AI developer. I review your app the way an attacker would, then explain and fix what matters, in order of risk.
WHAT I CAN CHECK AND FIX:
You get a clear report with each issue, its risk and the fix. Fixes are tested with separate user accounts and retested.
I work with Supabase, Firebase, Next.js, React, Vercel, Netlify, Stripe and other compatible tools. I test without touching your live user data unless you agree.
Please contact me before ordering so we can review your app and choose the right package.
Full Stack AI Developer, AI Agents, Apps, Integrations
Alex T. is part of the Fiverr Pro catalog and has been hand-picked by a dedicated Fiverr Pro team for their skills and expertise.
Vetted for
Website Maintenance
Languages

Aina Kari

Vitamina Lab

Lvnea Perfume

Medusa Jewelry
What exactly do you check in my app?
Supabase RLS policies, exposed API and service role keys, auth and admin flows, API routes, edge functions, webhooks, rate limiting, storage buckets and personal data exposure. I test as a stranger, a normal user and an admin to see what each one can really read
Which platforms and tools do you work with?
Apps built with Lovable, Bolt, Base44, Replit, Cursor, v0 or by hand, mainly on Supabase, but also Firebase, Postgres, Next.js, React, Node.js, Vercel and Netlify. If your stack is unusual, send me a message first and I'll confirm.
What do you need from me to start?
Usually read access to your code (GitHub or an export), your Supabase project or a copy of its schema, and test user accounts. For fixes I need permission to apply changes. You decide what I can access and you can revoke it at any time.
Will you touch my live data or users?
No, unless you agree. I work on your repo, a copy of the schema or a staging project whenever possible, and use test accounts. If a fix could break a feature, I explain it and we agree on the approach before applying it.
What is the difference between the three packages?
Basic is an audit with a report prioritized by risk. Standard adds fixes for critical and high risk issues, tested and retested. Premium covers full hardening with all agreed issues fixed. I'll recommend the right package once I see your app.
Can you fix the issues, or only report them?
Both. Basic gives you a clear report your team or AI tool can act on. Standard and Premium include the fixes as code and SQL migrations in your repo, so you keep them. Larger apps or extra work beyond the audit get a custom offer.
Will my app be 100% secure after the audit?
No one can honestly guarantee that. I find and fix the most common and serious issues in vibe coded apps and lower your risk a lot, but new code, new features and third-party services can add new risks over time.
Do you provide compliance certification (GDPR, SOC 2, HIPAA)?
No. This is a technical security review, not a legal or compliance certification. I flag personal data risks and handle your data securely, but compliance with GDPR or other rules remains your responsibility and your legal advisor's.
Are third-party costs included?
No. Supabase, hosting, rate limiting or monitoring services are paid directly by you through your own accounts. Most fixes use features you already have, and if a paid service is useful I'll explain why before you decide.
What happens after delivery?
You own the report, code and policies. I walk you through the findings and fixes, include essential notes on keeping new tables and features safe, and give 7 days of bug fixing on my changes. Ongoing checks and new work are available separately.
