Browse categories
Explore
Fiverr Pro
English
$
USD
AI Engineer
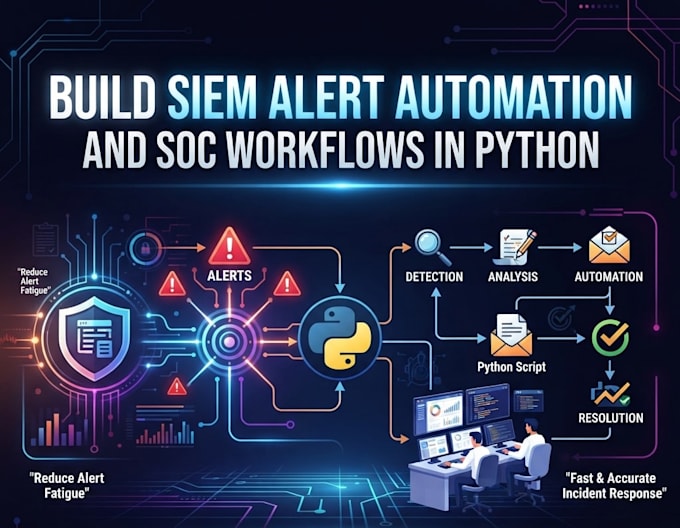
I build Python automation that connects your SIEM directly to your response workflow alert triage, log parsing, and threat intel enrichment, wired into Splunk or Sentinel so your analysts stop doing by hand what a script can do in seconds.
What I build:
I work specifically with Splunk and Sentinel. If your environment runs a different SIEM, message me first I'd rather confirm fit before you order than take a job I can't deliver well.
Message me before ordering with your platform (Splunk/Sentinel), the specific workflow you want automated, and roughly how many alerts/logs it handles per day that's the difference between Basic and Standard scope.


Which SIEM platforms do you work with?
Splunk and Sentinel, specifically. If you're on Wazuh, QRadar, Elastic, or another platform, message me before ordering so we can confirm whether I'm the right fit — I'd rather turn down a mismatched job than deliver something half-working.
Do I need to provide API keys or SIEM access?
Yes, for implementation. I'll walk you through using environment variables or temporary scoped credentials so you're not handing over standing access.
What's the difference between Standard and Premium?
Standard automates one alert-to-action pipeline on a single platform. Premium chains multiple systems — SIEM, threat intel, and ticketing/SOAR — together with MITRE ATT&CK mapping on top. If you're not sure which you need, message me your workflow and I'll tell you honestly.
Can you help with compliance automation?
Yes — scripted evidence collection for ISO 27001 and SOC 2 audit prep. This isn't a full audit or certification service; it automates the evidence-gathering grind, not the audit itself.
What language do you build in?
Python primarily, with Bash or PowerShell where the target system calls for it (e.g., Windows-based log sources).
What do you need from me to start?
Your SIEM platform, the specific alert or workflow you want automated, and sample log/alert data (anonymized is fine) so I can build against real structure instead of guessing at your schema.