Browse categories
English
$
USD
Connect to your AI
Design is not a philosophy, it's a life
Is your AI chatbot leaking data, getting jailbroken, or saying things it shouldnt?
Most AI developers build features. Few test whether those features can be attacked. I help you find the weaknesses in your AI app and fix them before they become a public problem.
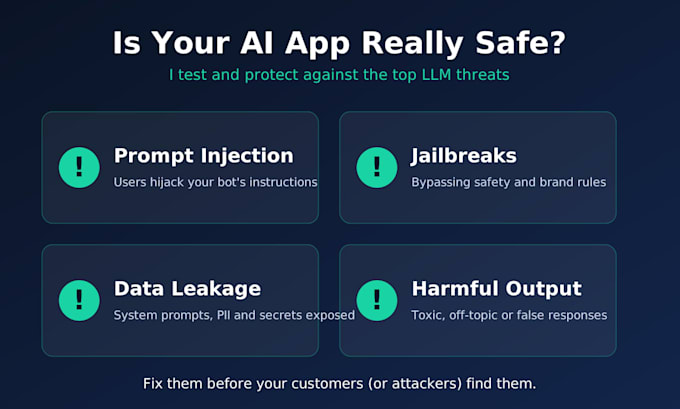
What I protect against:
What you get:
Who this is for: startups launching AI products, businesses with customer-facing chatbots, developers using LLM APIs, and agencies building AI tools for clients.
Before ordering, message me with your app type, the model you use, and what worries you most. Ill confirm the scope so there are no surprises
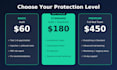
Do you need access to my code?
Not for Basic. I can test the app from the outside. Standard and Premium need some access to implement fixes.
Will you test my live product?
Only with your written permission, and I’ll agree on safe testing limits first.
What do I get at the end?
A report, plus working guardrails in the higher packages.