Browse categories
English
$
USD
Connect to your AI
Cybersecurity Specialist, Penetration Tester, Vulnerability Assessment
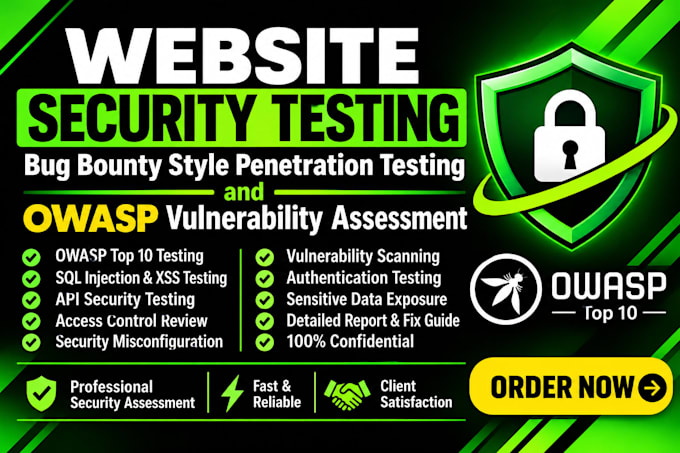
Are you looking for a reliable website security specialist to assess your website, uncover security weaknesses, and help protect your digital assets? I provide professional website security testing, ethical hacking, and bug bounty-style penetration testing to help identify potential risks and improve your web.site's security.
My services include:
Your web.site's security should never be left to chance. Identify vulnerabilities before malicious attackers can exploit them!
I follow recognized security testing methodologies and use industry-standard tools to assess your web site within an agreed scope.
Let's identify security weaknesses before attackers do.
Contact me today and let's work on how to strengthen your web site security!
Device:
Desktop
•
Laptop
•
Server
•
Mobile
•
Router
Operating system:
Windows
•
Linux
•
IOS
•
Android
•
Ubuntu
1. What types of website security testing do you offer?
I offer comprehensive website security assessments, including vulnerability scanning, manual penetration testing, OWASP Top 10 testing, bug bounty-style assessments, authentication testing, access control checks, API security testing, and security misconfiguration analysis.
2. Can you perform OWASP Top 10 vulnerability testing?
Yes! I can assess your website against the OWASP Top 10, covering common security risks such as Broken Access Control, Injection, Cryptographic Failures, Security Misconfiguration, and other relevant vulnerabilities.
3. Do you perform bug bounty-style penetration testing?
Yes. I conduct authorized, scoped security assessments using bug bounty-style methodologies to identify, validate, document, and explain security vulnerabilities.
4. Can you test websites built with WordPress, Shopify, or custom development?
Yes. I can assess various website platforms and technologies, including WordPress, Shopify, Laravel, PHP, React, Node.js, and custom-built web applications, depending on the available access and testing scope.
5. Do you test for SQL Injection and Cross-Site Scripting (XSS)?
Absolutely. I test for common injection vulnerabilities, including SQL Injection (SQLi), Cross-Site Scripting (XSS), and other relevant input-validation weaknesses using safe, authorized testing methods.
6. Can you perform API security testing?
Yes. I can assess REST APIs and other supported API endpoints for authentication weaknesses, authorization issues, excessive data exposure, injection risks, and other common API security vulnerabilities.
7. Do you test login systems and authentication security?
Yes. I assess login functionality, password security, session management, authentication mechanisms, authorization controls, and potential account access vulnerabilities.
8. Will I receive a detailed vulnerability report?
Yes. You will receive a professional report outlining identified vulnerabilities, severity levels, affected areas, supporting evidence, potential impact, and recommended remediation steps.
9. Do you provide vulnerability fixing and security recommendations?
Yes. I provide practical recommendations for addressing discovered vulnerabilities. Remediation or direct code fixes can also be discussed as an additional service depending on the project requirements.