Browse categories
English
$
USD
Connect to your AI
Nextjs and Supabase Developer for Vibe Coded App Rescue
Supabase security audit for AI-built apps: I check your RLS policies, auth and exposed keys before a missing policy leaks your customers' data.
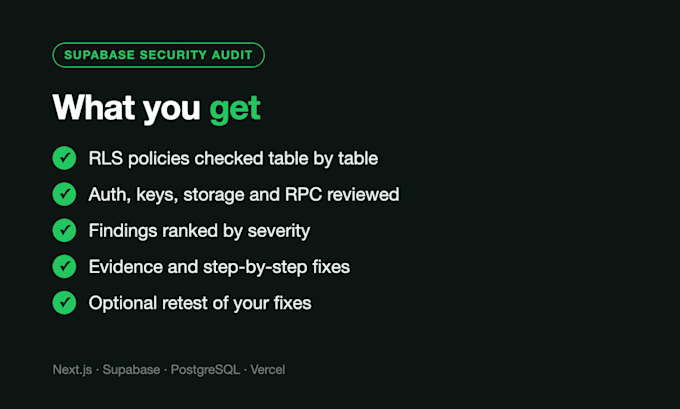
I review your Supabase project and send you a clear security report: findings ranked by severity (Critical / High / Medium / Low), with the evidence and the exact steps to fix each one.
What I check:
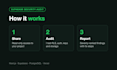
How it works: you give me read-only access, I review, you get the report and a short walkthrough. This gig is review only. If you want me to implement the fixes, I do that in my "fix and stabilize" gig or via a custom offer.
Stack: Supabase, PostgreSQL, Next.js, React, TypeScript, Vercel.
I run my own multi-tenant healthcare and ERP apps in production on this stack.
Please message me first with your project link so I can confirm scope.
Development technology:
TypeScript
Expertise:
Code efficiency
•
Data structure
•
Error handling
Do you fix the issues too?
This gig is the review: you get findings and exact fix steps. I can implement fixes through my "fix and stabilize" gig or a custom offer, but I never touch your code without a separate agreement.
What access do you need?
Read-only. A GitHub/GitLab read-only invite (or a zip of the repo) and, ideally, a read-only Supabase member role or exported schema and policies. I never need write access or your production keys.
Will you test my live production data?
No. I review code, configuration and policies. I do not read, export or modify your users' data.
Is the report something I can share with investors or clients?
Yes. It is written in plain language with severity levels, so you can share it with your team, investors or customers.