Browse categories
Explore
Fiverr Pro
English
$
USD

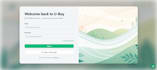
A poorly built auth system is a security risk I build it right the first time. From email/password login to OTP, Firebase, Clerk, and full RBAC, I've shipped this in production, including auth for a real-time platform load-tested for 1,000 concurrent users.
WHAT I BUILD
TECH STACK
Next.js, React, TypeScript, Node.js, Express, NestJS, Clerk, Firebase, Passport.js, NextAuth, MongoDB, PostgreSQL, Twilio
SECURITY
Bcrypt password hashing, JWTs in httpOnly cookies (never localStorage), rate-limiting against brute-force attempts.
Message me before ordering with your stack and preferred auth method I'll confirm the right package and timeline.
Modern fullstack website and web app development
Languages
Which auth method should I use — Clerk, Firebase, or custom JWT?
Clerk is best for Next.js projects where you want a fully managed solution with a beautiful UI and minimal setup. Firebase Auth is great for projects already using Firebase. Custom JWT gives you full control and works with any backend — best for complex role systems or when you want zero vendor depe
Can you add authentication to my existing application?
Yes — this is one of the most common requests I get. Share your current tech stack and I will integrate the auth system cleanly without breaking your existing code. I write modular auth middleware that plugs into your routes without restructuring your whole project.
Is the authentication secure enough for a production app?
Yes. Every system I build follows current security best practices — bcrypt password hashing, httpOnly cookie JWT storage, rate limiting on sensitive endpoints, input validation, and CORS configuration. I have built auth for production SaaS products, not just demo projects.
How is the code delivered?
You receive a GitHub repository with a clean folder structure, env variable setup instructions, and full documentation of every auth flow. You own the code completely.
Do you offer OAuth or MFA? Which tier?
Google OAuth is included from Standard up; MFA and audit logs are Premium-only.


