Browse categories
Explore
Fiverr Pro
English
$
USD
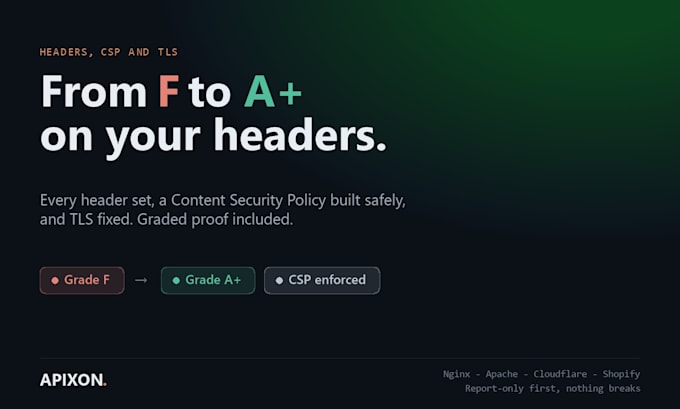
securityheaders.com gave you an F. Your client's security questionnaire asks about CSP. Or your payment provider wants to know what scripts run on your checkout. All the same job.
WHAT I DO
Set every header that matters, with values that fit your site rather than a copy-paste list
Inventory every third-party script on your site; most owners are surprised by the count
Build a Content Security Policy in report-only mode first, so nothing breaks
Watch the violation reports for a week, fix the policy, then switch to enforce
Fix TLS: 1.3, modern ciphers, correct chain, HSTS with preload if you want it
WHAT YOU GET
Your grade before and after, from securityheaders.com and SSL Labs, plus the full script inventory as a spreadsheet.
Why CSP matters more than people think: it is the control that stops a compromised third-party script from skimming your checkout. It is also the evidence behind the SAQ A eligibility criterion, which asks you to confirm scripts cannot put your payment page at risk.
Works on Nginx, Apache, Cloudflare Workers, Shopify, WordPress, Next.js and Vercel.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Website Security Fixes not just scans
Languages
Will CSP break my analytics or chat widget?
Not the way I do it. Report-only comes first and nothing is enforced until the violation reports are quiet.
I am on Shopify and cannot edit headers.
Some can be set, some cannot. Send me the URL first and I will tell you exactly which, then do what the platform allows.
Can you guarantee an A plus grade?
On most stacks yes. If your platform limits what can be set, I will say so before you order rather than after.
