Browse categories
Explore
Fiverr Pro
English
$
USD
Cybersecurity Consultant Specializing in SIEM and Compliance
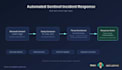
Automate your Microsoft Sentinel incident response with a working Azure Logic Apps pipeline, built for you, deployed by you.
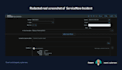
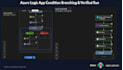
Incidents pile up, entity data sits buried in JSON, and manual triage eats your team's time. I'll build a Logic App automation that turns a real Sentinel incident into an automated response: entity extraction, optional threat-intel enrichment, and a notification or ticketing action.
What you get:
How it works:
Tell me your entity types and target action (Teams, email, webhook, or ticketing platform). I build and test the pipeline, then deliver the template plus docs.
Scope note:
This delivers a template for YOUR environment. I never require access to your live Sentinel workspace or credentials.
Background:
Hands-on Sentinel and Logic Apps automation, VirusTotal enrichment, conditional response logic, and OAuth-authenticated API integrations, tested end to end against a live ServiceNow instance.
Message me first if you're unsure which package fits.


Cloud provider:
Microsoft Azure
Q: Do you need access to my Sentinel workspace or security tools?
A: No. I build and test against realistic sample data, then deliver a template and setup guide for you to deploy in your own environment. I never need credentials or live access to your tenant.
Q: Do I need Sentinel already set up to order this?
A: It helps but isn't required. If you're still planning your deployment, I can build against standard Sentinel incident/entity shapes so the template is ready when you are.
Q: Premium mentions a custom platform integration — does that include ServiceNow specifically?
A: ServiceNow is one proven example (tested end-to-end, including real ticket creation). For a different platform, I'll research and adapt the same OAuth pattern to your target API as part of the Premium delivery.
Q: What if my target platform doesn't use OAuth?
A: Most modern APIs do, but if yours uses a different auth method (API key, Basic Auth, etc.), let me know in your order details so I can plan accordingly — this may affect delivery time
Q: Will this work with Microsoft Sentinel specifically, or other SIEMs too?
A: This gig is built specifically for Microsoft Sentinel's incident/entity structure and Azure Logic Apps. It isn't a generic SIEM-agnostic solution.
Q: Can you customize the severity threshold or entity types?
A: Yes — this is discussed during your scoping call and reflected in the delivered template. Standard and Premium tiers include this customization by default.
Q: Does this include the cost of Azure resources (Logic Apps, connectors, etc.)?
A: No — this gig covers the build and delivery only. Azure runtime costs (Logic Apps executions, API connections, any third-party API usage like VirusTotal) are billed to you directly by Microsoft/the relevant provider, separate from this gig.
Q: What if I run into issues deploying the template myself?
A: Each package includes revisions within its scope (see package details) to address issues with the delivered template. For ongoing support beyond that, we can discuss a separate arrangement.
Q: Will you need details about my organization or security setup?
A: Only what's necessary to scope the build correctly (entity types, target platform, any severity preferences) — nothing about your actual incidents, users, or infrastructure. I build against realistic sample data, not your live environment.
Q: What's your experience with Sentinel and Logic Apps?
A: I hold CySA+, CASP, and have hands-on experience building and testing Sentinel-integrated Logic App automations, including real entity extraction, threat-intel enrichment, and OAuth-authenticated API integrations against a live ServiceNow instance.


