Browse categories
English
$
USD
Connect to your AI
DevOps and DevSecOps Engineer AWS, Kubernetes
Are you worried about hackers stealing your code or injecting malware into your Docker images?
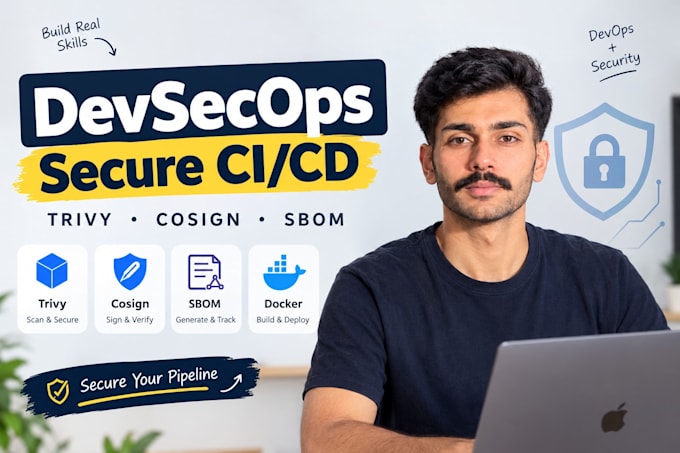
Many developers build fast CI/CD pipelines, but forget to secure them. As a DevSecOps Engineer, I will bake security directly into your deployment process without slowing you down.
What I will do for you:
Why choose me?
I am a dedicated DevSecOps Engineer with hands-on experience securing cloud environments (AWS) and Kubernetes clusters. I don't just build pipelines; I build secure pipelines.
Let's chat! Send me a message with your current setup before ordering.
️TOOLS
GitHub Actions, GitLab CI, Jenkins, Argo CD, Trivy, Cosign, Gitleaks, SonarQube, Docker, Kubernetes, Helm, Terraform, Ansible, AWS, Azure.
Tools:
Docker
•
GitLab
•
Jenkins
•
GitHub
•
Other
Frameworks:
Terraform
•
Ansible
Programming language:
Bash
•
C
•
Python
Expertise:
Installation
•
Development
•
Configuration
Will this slow down my deployments?
No. Security scans run in parallel where possible, and I tune thresholds to match your risk tolerance. Most pipelines add only 2–4 minutes to a build.
I already have a CI/CD pipeline. Can you add security to it?
Yes. I retrofit Trivy, Cosign, SBOM, and Gitleaks into existing GitHub Actions, GitLab CI, or Jenkins pipelines.
Do you work with private repositories?
Yes. Add me as a collaborator or provide temporary access. I sign an NDA on request.
What if I don't use Docker or Kubernetes?
The pipeline still works. I scan source code, dependencies, and artifacts even without containers. Message me with your stack and I'll confirm.
Which CI/CD tool should I choose?
If undecided, I recommend GitHub Actions for simplicity or GitLab CI for integrated security. I'll advise based on your existing stack.
Do I get the source code and configuration files?
Yes. Every pipeline file, scan config, and documentation is handed over to you, you own everything.
What if something breaks after delivery?
Premium includes 7 days of post-delivery support. For Basic and Standard, I offer one free fix within 3 days of delivery.
