Browse categories
English
$
USD
Connect to your AI
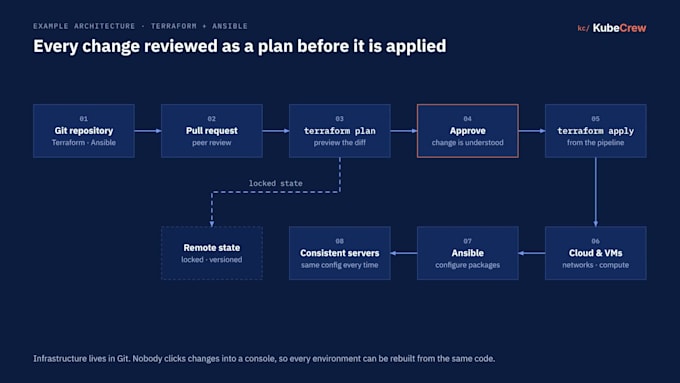
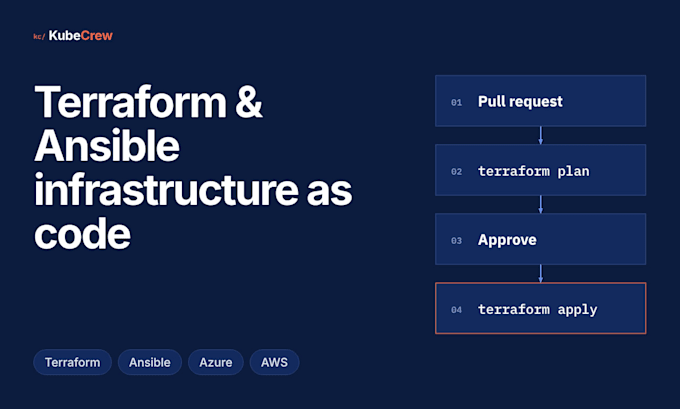
Clicking changes into a cloud console works until nobody remembers what changed. I'll put your infrastructure in Git, so every change is reviewed as a plan before it's applied.
What you get:
Terraform modules for networks, compute and databases
Remote state, versioned and locked
terraform plan posted on every pull request
Apply only from the pipeline, after approval
Ansible roles so every server gets the same config
Drift detection that flags console changes
Docs your team can follow
Clouds: Azure and AWS. CI: GitHub Actions, GitLab CI, Azure DevOps
How I work:
1. Understand: what exists today and what must not break
2. Plan: a clear sequence with visible trade-offs
3. Leave it maintainable: modules your team can extend
Security: I only use least-privilege access you create for me. State files and secrets stay in your account.
Not sure which package fits? Message me with what you run today before ordering.

Tools:
Docker
•
GitLab
•
GitHub
•
CircleCI
•
BitBucket
Framework:
Npm
•
Terraform
•
Pulumi
•
Ansible
•
Chef
Programming language:
Bash
•
Python
•
Golang
•
PowerShell
•
Other
Expertise:
Installation
•
Migration
•
Configuration
Can you bring my existing resources into Terraform?
Yes, with the import extra. I import them into state and confirm terraform plan shows no changes before anything is applied.
Where does the state live?
In your account: an Azure Storage container or an S3 bucket, with locking. Nothing is stored on my side.
Do I need Ansible?
Only if you run VMs. For managed services and containers, Terraform alone is usually enough.
Will applying break production?
Every change is shown as a plan first and applied only after you approve it. Risky changes go to staging first.