Browse categories
English
$
USD
Connect to your AI
Not sure what your team should do when a security incident hits? Get a ready-to-use incident response playbook in Notion, so everyone knows who does what, and when.
Built by a computer science and engineering graduate with hands-on SOC/IR training (Commonwealth Bank virtual job simulation, SOC lab).
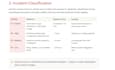
BASIC: core essentials: activation criteria, P1-P4 severity matrix, roles, triage and containment steps.
STANDARD (most popular): the full playbook:
Severity matrix, roles, triage, evidence handling, containment
Out-of-band comms plan and contact sheet
Regulatory reference (GDPR, HIPAA, CERT-In, UK GDPR, PIPEDA, PDPA, NIS2 and more)
Recovery, post-incident review, comms templates
Ransomware quick annex
Incident Log database
ISO 27001 / SOC 2 mapping (reference)
PREMIUM: Standard, customized with your roles, severity levels, and a RACI/escalation plan.
Best for startups, small security teams, and consultants.
Starting reference only, not legal advice or a compliance guarantee. Confirm with your own counsel or auditor.


Please inform the freelancer of any preferences or concerns regarding the use of AI tools in the completion and/or delivery of your order.
Will I be able to edit the template after I get it?
Yes, fully editable once duplicated.
Do I need a paid Notion plan?
No, free plan works fine.
Is this based on a specific compliance framework?
Yes — aligned with NIST SP 800-61r2 and includes ISO 27001/SOC 2 control mapping.
How is this delivered?
Notion duplicate link, ready instantly.
Found a mapping that doesn't fit your framework version?
Message me and I'll update it
What's the difference between the packages?
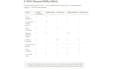
Basic covers core response essentials (activation, severity, roles, triage, containment). Standard adds evidence handling, regulatory reference, recovery, comms templates, and a working tracker. Premium adds compliance mapping plus a full severity, escalation, and RACI expansion
Is the compliance mapping audit-certified?
No. The ISO 27001:2022 and SOC 2 mapping is a verified starting reference to speed up your prep, not a certification guarantee. Always confirm final control mappings with your own auditor before submitting as audit evidence
Are the regulatory timelines legally guaranteed?
No. Reporting windows for GDPR, CERT-In, PIPEDA, and others are provided as a starting reference and are verified at the time of writing, but they change. Confirm current obligations with your own legal counsel before relying on them.
Do you offer revisions?
Yes, revisions per package are listed in the pricing table. Message me first if you need something outside standard customization, like an industry-specific version.


