Browse categories
Explore
Fiverr Pro
English
$
USD
Are you preparing for ISO 27001:2022 certification or looking to strengthen your organization's Information Security Management System (ISMS)?
As a certified ISO 27001 Lead Auditor / Implementer with hands-on experience in enterprise cybersecurity (endpoint protection, DLP, access control, and IT infrastructure), I provide structured, practical, and audit-ready ISO 27001 consulting tailored to your business needs.
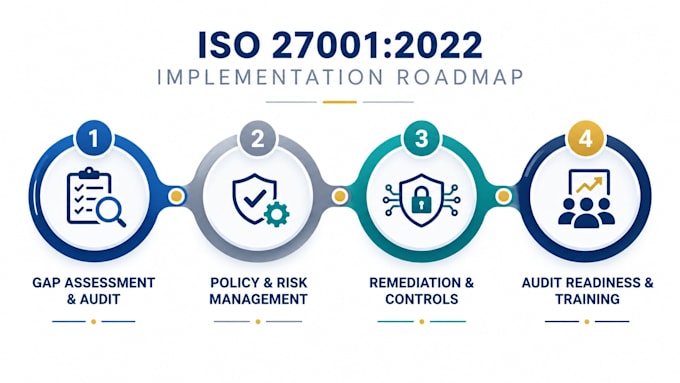
What I can help you with:
Why choose this Gig?
Please contact me before placing an order so we can discuss your sp
Do you provide actual ISO 27001 certification?
No, official ISO 27001 certificates can only be issued by an accredited Certification Body (CB). I help you prepare your organization, documentation, and controls so you pass the official audit smoothly.
Can you customize the documentation to my company’s size?
Absolutely. I tailor all policies and risk assessment frameworks to fit your specific operational size, infrastructure, and industry requirements.
What do you need from me to start?
A brief overview of your current IT setup, existing security policies (if any), and the scope of your target ISMS.