Browse categories
English
$
USD
Connect to your AI

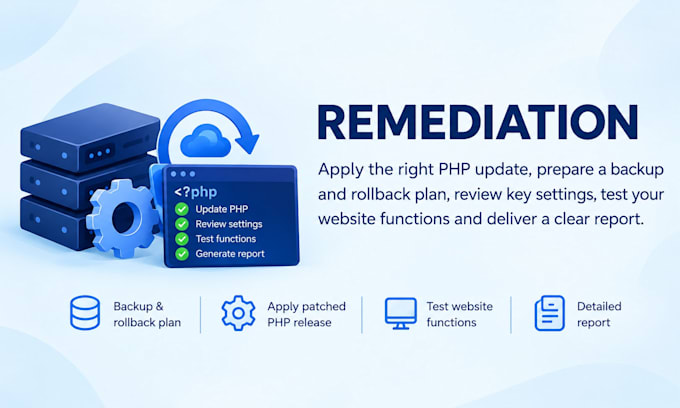
Concerned about PHP2Shell? I will review your PHP setup and help remediate CVE-2026-109618 and CVE-2026-109619 with official or vendor-supported security updates.
I have 7 years of web development experience, including PHP, WordPress, Laravel, VPS deployment and Docker.
Depending on your package, I will:
Basic is assessment only. Standard covers one compatible website. Premium adds staging and up to 2 hours of agreed compatibility fixes.
Older PHP versions, multiple websites and major code upgrades require a custom quote. Shared hosting updates may depend on your provider. Malware cleanup and full penetration testing are not included. Temporary mitigations are not a complete replacement for patching.
Message me with your website URL, hosting type and PHP version before ordering so I can confirm scope and access.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Senior Full Stack Developer, Custom Web Apps and WordPress
Languages
What does this PHP2Shell service cover?
It covers assessment and, in patch packages, remediation of CVE-2026-109618 and CVE-2026-109619 using official or vendor-supported PHP updates. Package scope determines backups, application testing, staging and compatibility work.
Does the Basic package include fixing the issue?
No. Basic checks one website's PHP runtime and patch status and provides a written action plan. Choose Standard or Premium for an agreed update, or message me for a custom offer.
Do you support WordPress, WooCommerce and Laravel?
Yes, as well as custom PHP applications. I review the hosting setup, dependencies and required access before confirming the update scope. Large stores and older applications may need a custom offer.
Will updating WordPress or installing a security plugin fix PHP2Shell?
Updating WordPress or adding a security plugin alone does not patch the PHP runtime. I check the PHP build serving your website and whether your hosting vendor has applied the relevant fixes.
Can you disable a PHP feature instead of updating?
Temporary configuration changes may reduce specific risks, but they are not a complete substitute for the PHP2Shell patches. I explain any remaining exposure and prioritize an official or vendor-supported update.
What if I use shared hosting or an older PHP version?
On shared hosting, the provider may control PHP updates. Older branches require compatibility review and confirmation of any vendor backport. I assess the available options before accepting a fixed-price patch order.
Will my website have downtime or compatibility problems?
Updates can require a restart or maintenance window. I prepare backup and rollback steps and test agreed workflows. Premium adds staging and limited compatibility fixes. Zero downtime and compatibility with all legacy code cannot be guaranteed.
What if my website is already patched or has been hacked?
If already patched, I document the evidence and avoid unnecessary changes. Malware removal and incident response are separate services; a PHP update alone cannot prove that an existing compromise has been removed.
What access do you need?
Depending on your setup, I may need temporary hosting access, limited SSH access and a website admin or test account. I confirm requirements in the order conversation. Share only necessary access and revoke it after completion.
What will I receive, and what counts as a revision?
You receive a report of findings or changes, patch evidence, agreed tests and remaining actions. Revisions cover the original scope. Extra sites, new features, major migrations, full penetration testing and paid licenses are excluded.