Browse categories
Explore
Fiverr Pro
English
$
USD



Your upload returns 403 and the message says row-level security policy. The policy looks correct. It usually is.
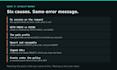
What is actually happening is one of six things: the request arrives without a session so it lands as anon, the insert is judged by WITH CHECK and not USING, the path prefix is not what the policy expects, upsert and resumable uploads need an UPDATE policy as well, signed URLs need SELECT, or a grant underneath the policy is missing and returns the same 403.
I find which one it is, fix it, and prove it: the same upload from your own client, before and after, with the response printed next to it.
You get the migration, one line on what was actually wrong, and a check on what still blocks a stranger, so the fix does not quietly open your bucket to everyone.
Send me the exact error, the policy SQL, the bucket name, and how your client is created. A staging copy or a read-only role is enough. I do not need your service role key.
I build a multi-tenant POS on Supabase, around 90 migrations, live in real shops. Three security reviews on it found six real holes, every one past policies that were correct as written.
Supabase RLS and privilege audits
Languages
Can you just make my bucket public and be done?
No. That removes the error by removing the security, and it also does not help uploads, since a public bucket still needs an INSERT policy. If the bucket genuinely should be public I will tell you and it takes two minutes, but I will not do it silently to close a ticket.
Do you need my service role key?
No, and I would rather not have it. A read-only role, or a staging copy with the same schema, is enough to find the cause. When a write is needed I send you the migration and you run it. You can revoke whatever you gave me the moment we are done.
I use Clerk or a custom JWT, not Supabase Auth. Does that change anything?
It is covered, and it is one of the more common causes. The claim your policy reads is often not the claim the token actually carries, so auth.uid() comes back null or wrong and every upload fails while the login itself looks fine.
What if the problem turns out not to be storage at all?
I tell you, with the query that shows it, and you decide whether to continue. I will not invent a storage finding to justify the order, and if there is nothing here worth paying for I will say so before you spend more.


