Browse categories
Explore
Fiverr Pro
English
$
USD

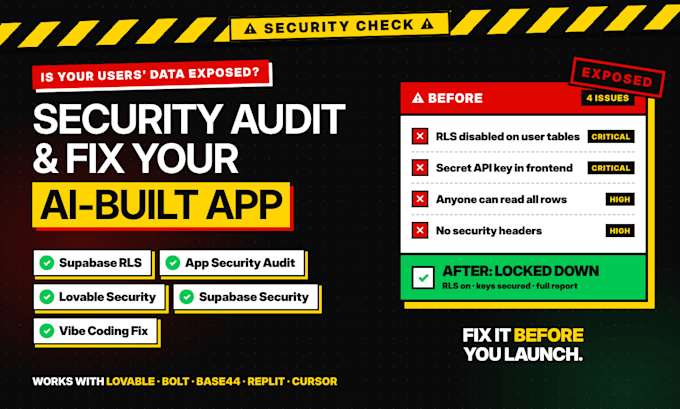

Built your app with Lovable, Bolt or Base44 and connected Supabase? Check it before you launch.
AI builders often ship apps with Row Level Security turned off or API keys exposed in the frontend. That can let anyone read or change your users' data. Public leaks of AI-built apps have already exposed thousands of user records.
I audit your app and fix the holes:
Supabase RLS check on every table
Fix or write RLS policies so users only see their own data
Scan for exposed API keys and secrets
Move secret keys out of the frontend
Check login, auth and admin access
Security headers review
Clear report: what was wrong, what I fixed, what's left
Works with Lovable, Bolt, Base44, Replit, Cursor and v0 apps using Supabase.
Message me before ordering and I'll tell you which package fits your app.
Note: I only audit apps you own or have permission to test. An audit lowers your risk a lot, but no one can honestly promise an app is 100% secure.
Software Developer
Languages
Will fixing RLS break my app?
It can if it’s done carelessly, because the app may have been relying on open access. I test every feature after adding the policies and fix anything that stops working.
Do you need my Supabase password?
No. Invite me to your Supabase project as a team member, and remove me when the job is done.
What if you find an exposed key?
I’ll tell you right away so you can rotate it (generate a new one). An exposed key should be treated as already compromised.
Does it work without Supabase?
Mostly yes. Firebase and other backends get the same checks, but message me first so I can confirm.
