Browse categories
Explore
Fiverr Pro
English
$
USD
Stop letting your AI agent run with more GCP access than it needs.
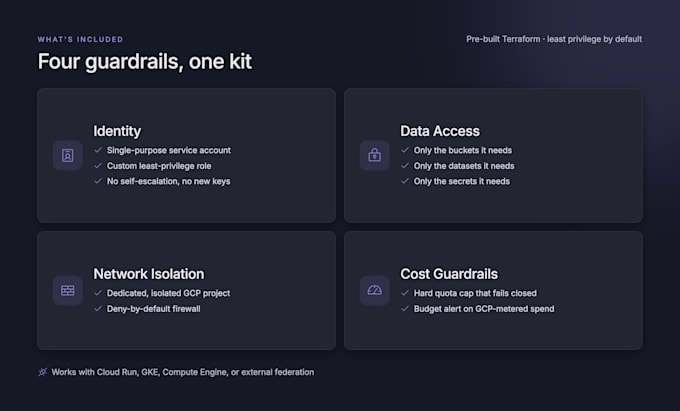
I'm a UK-based Senior Platform Engineer specialising in GCP. This is a pre-built Terraform kit that gives your AI agent least-privilege identity, scoped data access, workload isolation, and cost guardrails - no access to your environment required.
What you get:
Works with GCP-native workload identity (Cloud Run, GKE, Compute Engine), external federation, or a flagged fallback key as last resort.
Honest scope note: this covers GCP-metered spend only (Compute, Vertex AI). Direct calls to an external LLM provider aren't visible to GCP's own controls.
Basic gets the composition alone. Standard adds a permissions and quota worksheet. Premium adds a video walkthrough and priority support.
Message me with any questions before ordering.


Tools:
GitHub
Framework:
Terraform
Cloud Provider:
Google Cloud Platform
Programming language:
Other
Expertise:
Installation
•
Debugging
•
Configuration
Do you need access to our GCP project or agent code?
No to both. It's delivered as Terraform you apply yourself with your own credentials -- that's also why it's fixed-price, not hourly.
Does this work with LangChain, CrewAI, n8n, or our own agent code?
Yes. This works one layer below your agent's framework, at the identity layer, where GCP only cares how the caller authenticates -- it doesn't matter what's driving the reasoning.
What Terraform version does this need?
Terraform >= 1.5. I'll confirm the exact version I've tested against once I've run a full live deploy cycle, before this goes live.
Is this production-ready?
Every module has passed its own README review and terraform validate. I'll run a full live deploy and teardown test before launch, the same way I did for my other GCP kit.
What if we need something outside the standard scope after delivery?
Happy to quote it separately -- message me and we'll scope it properly.
Does this cover cost from other AI providers like OpenAI or Anthropic?
No -- only GCP-metered spend. Direct calls to an external LLM provider aren't visible to GCP's billing or quota controls at all.