Browse categories
Explore
Fiverr Pro
English
$
USD
AI, Computer Vision, and Full Stack Developer
Need source code recovery from an EXE, DLL or APK you own?
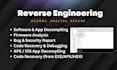
I provide professional reverse engineering, decompilation and binary analysis to recover readable code, application logic and undocumented software behavior.
I can work with EXE, DLL, APK, ELF, SO, JAR, .NET assemblies and native binaries.
What I can deliver:
Tools may include Ghidra, IDA, x64dbg, dnSpy and JADX.
Exact original source is not always recoverable because compilation can remove variable names, comments and metadata. I focus on accurate, usable reconstruction.
Please message me before ordering so I can confirm feasibility and scope.
Can you recover the exact original source code?
Not always. Compilation can remove original variable names, comments, formatting, symbols and metadata. Depending on the target, I can recover readable decompiled code, application logic, algorithms, classes, functions and pseudocode, or reconstruct selected components into maintainable source code.
Which files and platforms can you reverse engineer?
I can analyze many EXE, DLL, APK, ELF, SO, JAR and .NET binaries across Windows, Linux and Android, including x86, x64 and ARM targets. Send your file before ordering and I will confirm feasibility.
Should I order a package immediately?
Please message me first. Reverse-engineering complexity varies significantly depending on the binary, compiler, architecture, obfuscation and required output. I will review the scope and recommend the correct package or custom offer.


