Browse categories
Explore
Fiverr Pro
English
$
USD
Ethical Hacking, Web Security
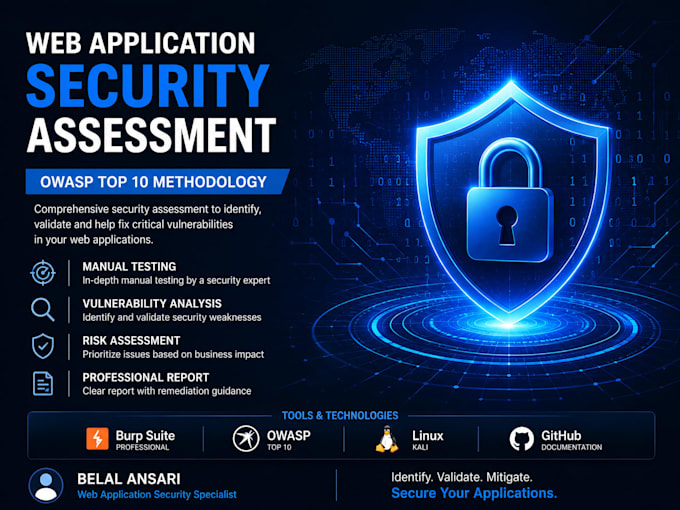
I will perform a professional web application security assessment using a structured OWASP Top 10 methodology to identify, validate, and document security weaknesses in your web application.
Testing covers manual security testing, vulnerability identification and validation, attack-surface analysis, security impact assessment, evidence collection, and clear reporting with practical remediation guidance.
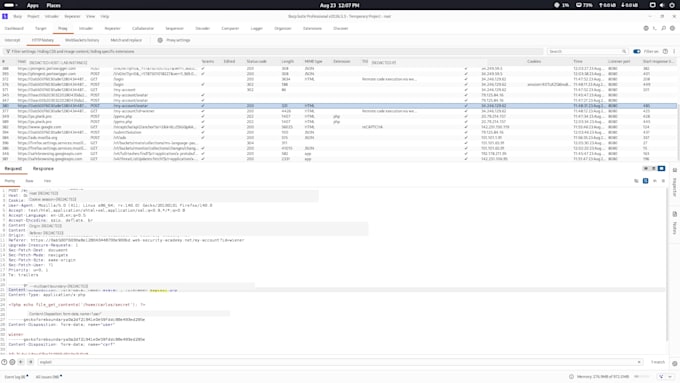
Testing was performed in authorized laboratory environments, client-approved environments, and PortSwigger Web Security Academy laboratory environments. Burp Suite Professional and manual testing techniques were used to investigate application behavior and validate security findings.
Depending on the selected package, you will receive a security summary report, annotated screenshots, validated findings, risk assessment, and actionable remediation recommendations.
I focus on responsible, evidence-based security testing and do not perform testing against systems without proper authorization.



_upzvst.jpg)
Testing application:
Web application
Development technology:
HTML & CSS
•
JavaScript
•
PHP
•
Python
•
SQL
Device:
PC
•
Linux
What do you need from me to start the security assessment?
I need the target website or application URL, the agreed testing scope, and written authorization to perform security testing. If authentication is required, please provide the necessary test credentials and any relevant scope limitations.
What types of vulnerabilities do you test for?
I test for common web application security weaknesses using an OWASP Top 10–aligned methodology, including injection, authentication and access control issues, security misconfigurations, XSS, CSRF, file-related vulnerabilities, SSRF, and other applicable weaknesses within the agreed scope.
Do you perform manual security testing?
Yes. The assessment uses manual security testing techniques with Burp Suite Professional to investigate application behavior, validate potential vulnerabilities, and reduce false positives. Automated tools may be used where appropriate, but findings are manually reviewed.
Will I receive a security report?
Yes. Depending on the selected package, you will receive a security summary or detailed report containing validated findings, supporting evidence, risk information, and practical remediation recommendations.
Can you test my website without authorization?
No. I only perform security testing on applications and systems where the client has provided proper authorization or where the environment is specifically designed for security testing, such as PortSwigger Web Security Academy laboratories.