Browse categories
Explore
Fiverr Pro
English
$
USD


Built your app fast with Lovable, Bolt, Cursor or by hand, and now real users are coming? Before they do, let someone look at it the way an attacker would.
WHAT I CHECK
- Secrets in the repo and Git history (.env, API keys, tokens)
- Authentication and sessions: cookies, JWT, expiry, revocation
- Access control on API routes and server actions: can a user reach what isn't theirs?
- Input validation and injection (SQL, XSS, SSRF)
- Security headers, CORS, CSP, rate limiting
- Dependencies with known vulnerabilities
- Error handling: what leaks to the browser
WHAT YOU GET
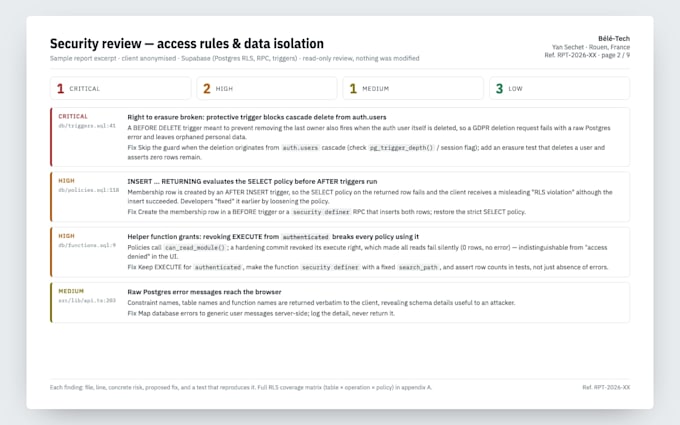
- A written report ranked critical / high / medium / low, with file, line, concrete risk and the fix
- Steps to reproduce each finding
- Premium: fixes delivered as pull requests you review, one per finding
HOW I WORK
Read-only unless you order fixes. No production access, no real user data. Fixed scope and price, written exclusions. Replies within 24 h.
Background: I run a production health-data app (Next.js, Postgres, Docker) with end-to-end encryption, WAF, monitoring and tested backups.
Not sure which package fits? Send me the repo size and stack, I'll tell you honestly.
Supabase RLS App Security Auditor Web Developer
Languages