Browse categories
English
$
USD
Connect to your AI
Cybersecurity Analyst SOC and Splunk SIEM
Do you need help making sense of your security logs?
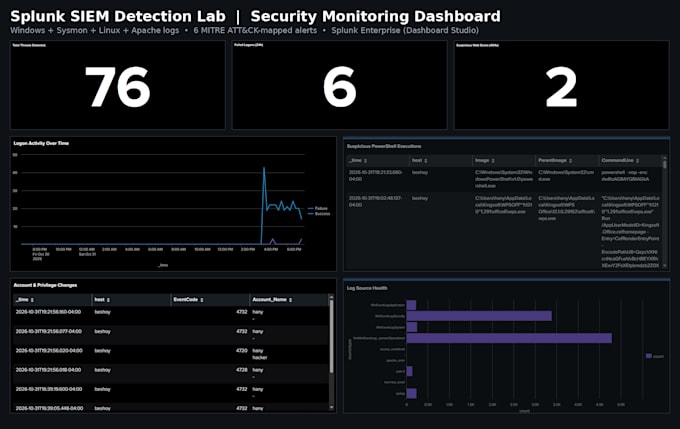
Reading through thousands of Splunk log entries is time-consuming. As a certified SOC Analyst (CEH, CSA, ECIR), I can review your logs, identify suspicious behavior, and provide a clear, easy-to-read report on what I found.
What I will do for you:
- Review your exported Splunk logs.
- Hunt for suspicious activity (e.g., brute-force attacks, failed logins, privilege escalation).
- Run SPL queries to filter out the noise and find the real threats.
- Provide a written report explaining any anomalies I find and recommend next steps.
What I need from you:
- A sample of the logs you want me to analyze (CSV or text format).
- A brief description of your environment (e.g., Windows, Linux).
Why choose me?
I am deeply passionate about Blue Team defense. I don't just run tools; I understand the MITRE ATT&CK framework and the incident response lifecycle. Let me help you secure your environment.


Technology:
Splunk
•
Other
Analysis type:
Diagnostic analysis
•
Other
Expertise:
Alerts
•
Anomaly detection
•
Other
Programming language:
Python
•
SQL
What format should my logs be in?
CSV, TXT, or JSON format is best. If you are unsure, please message me before ordering.