Browse categories
Explore
Fiverr Pro
English
$
USD
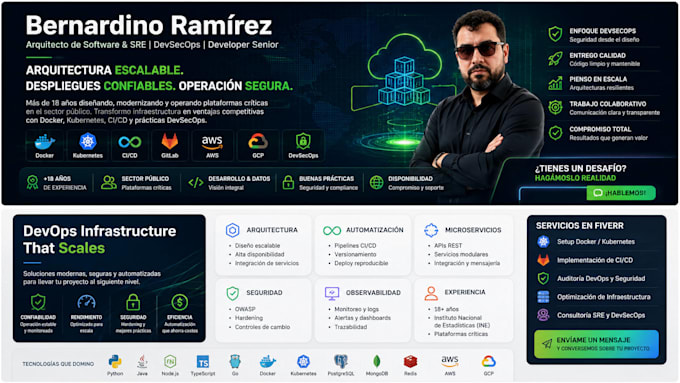
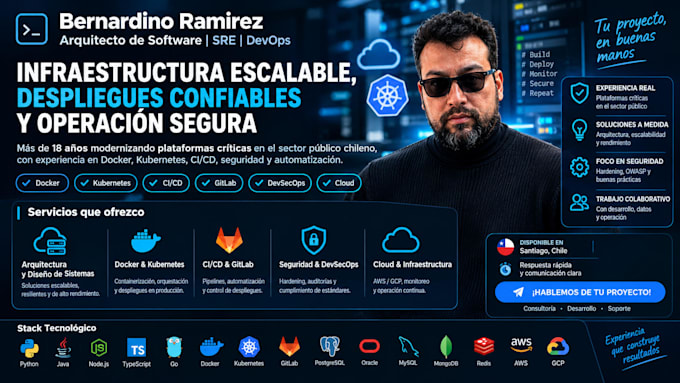
Arquitecto de Software y SRE, Docker Kubernetes CI CD
As a senior software architect and SRE with 18+ years of experience, I help teams secure their infrastructure and development pipelines before vulnerabilities become incidents.
What I offer:
- Security audits of cloud infrastructure (AWS, GCP)
- CI/CD pipeline security review (GitLab, Docker, Kubernetes)
- IAM and access control assessment
- Container and secrets management hardening
- Monitoring and alerting setup for security events
- Actionable remediation plans with clear priorities
I have hands-on experience securing production-grade platforms including GitLab CI/CD pipelines, LDAP integration, and containerized microservices architectures. My goal is to give you a clear, practical roadmap to reduce risk without slowing down your delivery pace. Let's make your systems resilient together.

Tools:
Docker
•
GitLab
•
Opsera
Frameworks:
Terraform
•
Ansible
Cloud Provider:
Amazon Web Services
•
Google Cloud Platform
Programming language:
Bash
•
Java
•
JavaScript
•
Python
Expertise:
Debugging
•
Development
•
Configuration
Do you need access to my production environment?
For audits, read-only access is sufficient in most cases. For hands-on remediation packages, I'll coordinate secure, temporary access following your security policies and least-privilege principles.
What deliverables will I receive?
A detailed report covering findings, risk levels, and prioritized remediation steps. Premium tier also includes hands-on fixes and follow-up consultation calls to walk through the results.