Browse categories
Explore
Fiverr Pro
English
$
USD



Your AI agents can reach Jira, GitLab, Slack and your databases. Can you say what they did today, and who asked them to?
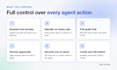
I build AI agents and automations with a control layer in between, so agents never hold your keys and every action is scoped, approved and logged. I run this setup in production on my own platform.
What you get:
Works with Claude, GPT, Gemini, n8n, MCP clients and your dev tools (Jira, GitLab, GitHub, Slack).
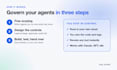
How it works:
Self-hosted on your own cloud if you need it. You own all the code and logs.
Not sure where to start? The Basic package is an audit of what your agents can access today, with a fix plan.
AI and Compute infrastructure
Languages
Does this work with the AI tools we already use?
Yes. The control layer sits between any agent (Claude, GPT, Copilot, n8n or MCP clients) and your tools. You keep your agents and add control over what they can do.
What does the audit include?
I review which agents you run, what each can access, where the keys live and what gets logged. You get a written report ranking the risks, plus a fix plan you can do yourself or hand to me.
Do you need access to our systems?
For the audit, a screen-share walkthrough or read-only access is enough. For builds, I work in your accounts with scoped access you can revoke at any time.
Where are the audit logs stored?
In your own database or cloud, out of the agent's reach. You own them and decide how long to keep them.
Will this slow our agents down?
Not noticeably for normal use. Only the actions you mark as high-risk wait for a human approval.
Can it run on our own cloud?
Yes, and that's the default. Everything runs in your cloud account or on your servers, and you own all the code and logs.
Is this a compliance certification?
No. I build the technical controls and audit trail that frameworks like SOC 2 or ISO 27001 rely on, but I don't issue certifications.


