Browse categories
Explore
Fiverr Pro
English
$
USD
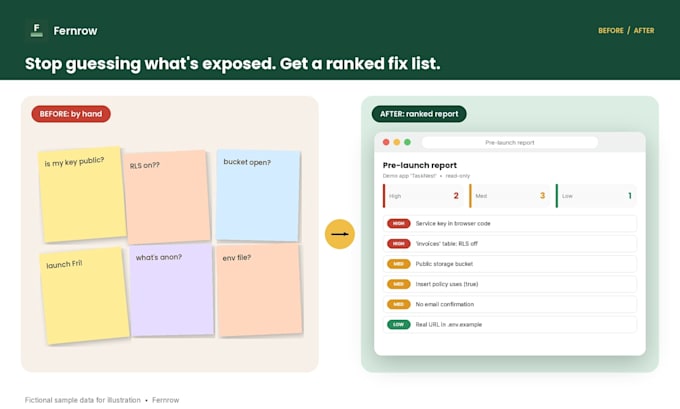
Stop guessing whether your AI-built app is leaking keys or data. We do a read-only check of your Lovable or Supabase app and send a report with every finding ranked by risk and a plain-English fix.
We review your live app and code (read-only) and send a clear report:
- What we checked and what we found, ranked by risk
- Plain-English steps to fix each issue
- A short checklist to re-test after fixes
What we need: your app URL and read access to the repo (GitHub invite) or an exported zip. We never ask for passwords, and we don't change your code in Basic or Standard.
Important: this is a focused pre-launch check, not a full penetration test or security certification. No guarantee an app is free of all vulnerabilities.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Bookkeeping Sheets and Store Automations
Languages
Do you edit my code?
Only in Premium, for one deploy error, and only with your OK.
Which stacks?
Lovable/Supabase best; Bolt, Cursor, Next.js on Vercel also fine.
Is this a pentest?
No. See note above.