Browse categories
Explore
Fiverr Pro
English
$
USD
programming and tech
Is Your Website Accidentally Exposing Sensitive Secrets?
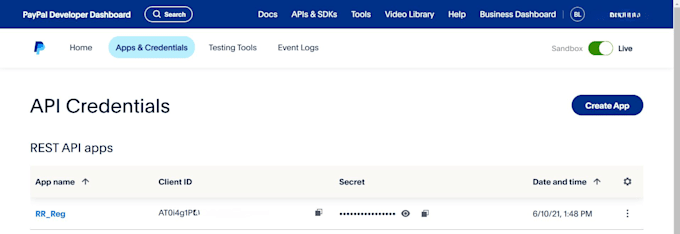
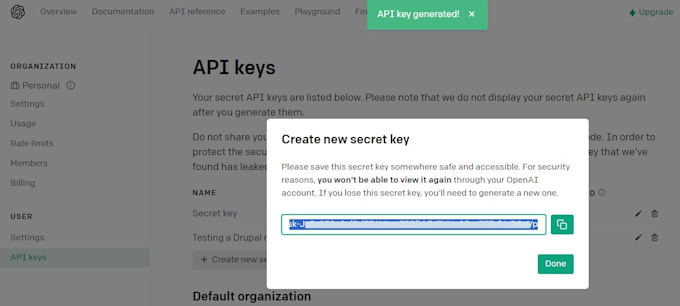
A publicly accessible API key, token, or credential can create a serious security risk if it is unintentionally exposed in source code, client-side files, repositories, configuration files, or other accessible resources.
I can help scan your authorized website or codebase for accidentally exposed secrets, identify potential security risks, and provide clear recommendations for fixing them.
️ What I Can Help With
Why Choose This Service?
Protect Your Digital Assets
Even an accidentally exposed development key or token can become a security problem. Identifying exposed secrets early allows you to revoke, rotate, and properly secure affected credentials before they are misused.
Contact me before placing an order with details about the authorized target and scope. I'll review your requirements and recommend the appropriate package.
What types of secrets can you look for?
Depending on the scope, I can check for API keys, access tokens, hardcoded credentials, private configuration values, and other sensitive strings.
Can you scan my website's source code?
Yes. I can review publicly accessible resources or authorized code provided for the assessment.
Can you scan a private codebase?
Yes, if you provide authorized access or the relevant files for review.