Browse categories
English
$
USD
Connect to your AI
I will perform a professional security code audit of your codebase and deliver an evidence-driven findings report.
What you get:
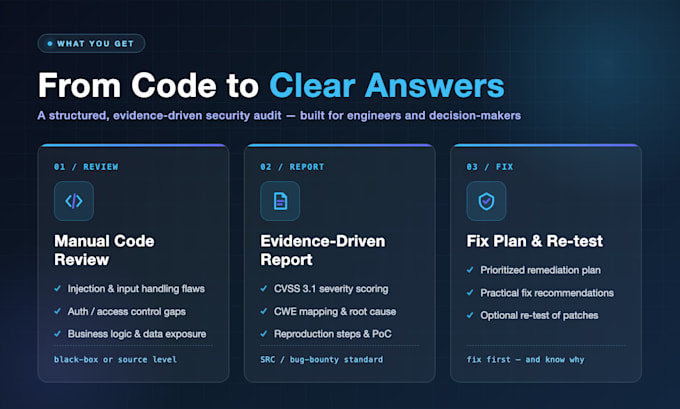
- Manual security code review: injection, auth/authorization flaws, business logic issues, insecure data handling
- Structured report: CVSS 3.1 severity, CWE mapping, reproduction steps, root-cause analysis, practical fix recommendations
- Prioritized remediation plan: what to fix first and why
How it works:
1. You share the code (repo or archive) and a short scope note
2. I audit and deliver the report within the agreed delivery time
3. Optional re-test of your fixes (add-on)
Scope: Python and web applications are my core expertise. Other stacks welcome - message me first.
Confidentiality: your code is used only for this audit and deleted after delivery.
I use AI tools for research and drafts; every deliverable is reviewed and verified by me before it reaches you.
Message me before ordering to confirm scope.

Development technology:
Python
Q1: What languages do you audit?
A1: Python and web applications are my core expertise. Other stacks are welcome - message me before ordering.
Q2: How do I send you my code?
A2: After ordering, share a private repo link or archive (zip/tar). Your code is used only for this audit and deleted after delivery.
Q3: What does the report include?
A3: Each finding has: severity (CVSS 3.1), CWE mapping, reproduction steps, root cause, and practical fix recommendations - in the standard format used by bug-bounty and SRC programs.