Browse categories
English
$
USD
Connect to your AI
CURLY SECURITY Web app Testing, Automation Specialist
Stop paying for automated scanner reports. Most gigs just run automated tools and export PDFs full of false positives. That isn't real security.
Welcome to Curly Security. I specialize in manual web application penetration testing. I think like an attacker to find the critical business logic flaws and access control bypasses (like IDOR and Privilege Escalation) that scanners miss.
What I Do:
Methodology: I perform Black-Box (no credentials) and Gray-Box (authenticated) testing to provide a realistic view of your security posture.

Testing application:
Web application
Device:
PC
•
Linux
Do you just run automated scanners like Nessus or Acunetix?
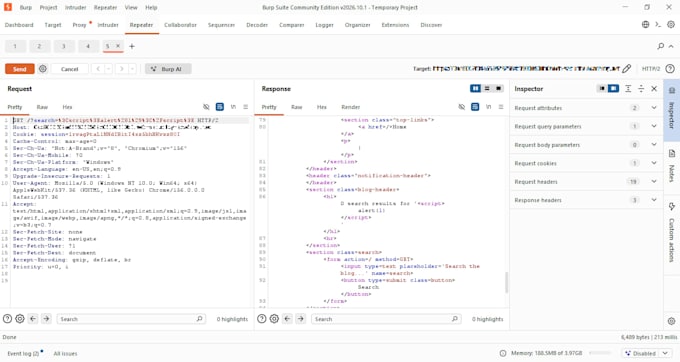
Absolutely not. I perform deep, manual testing using Burp Suite and custom Python scripts. Automated scanners miss complex business logic flaws (like user privilege escalation), which is exactly what Curly Security specializes in finding.
What exactly will I receive at the end of the gig?
You will receive a professionally formatted, highly confidential PDF report. It includes an executive summary, a breakdown of vulnerabilities by severity (CVSS), a step-by-step Proof of Concept (with screenshots showing the exploit in action), and exact remediation steps for your developers.
Do you need access to my source code?
No. I interact with your web application from the outside, exactly like a real malicious hacker would. However, providing a standard test user account (Gray-Box testing) is highly recommended so I can test authenticated features.
Will your testing crash or break my website?
No. I use safe, non-destructive testing methodologies. I do not perform Denial of Service (DoS) attacks, and I take extreme care not to disrupt your live database or impact your real users.
Can you test any website I want?
I can only test web applications that you personally own or have explicit, written authorization to test. You will be required to confirm your authorization before I begin any active reconnaissance.