Browse categories
Explore
Fiverr Pro
English
$
USD
IT Support and cybersecurity
I'll set up centralized log collection and monitoring for your business so you have visibility into what's happening across your network before a small issue becomes a big one.
Most small businesses have zero visibility into their systems until something breaks or gets compromised. I build the same kind of monitoring setup used in enterprise security operations, scaled down to fit a small environment.
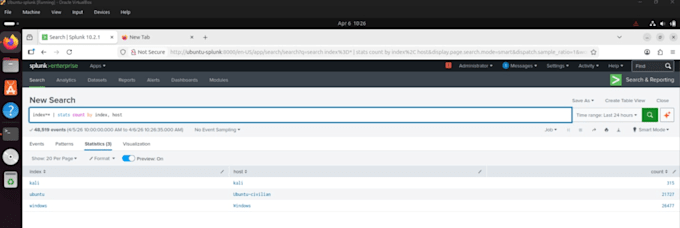
What I bring: Hands-on experience building and maintaining a multi-machine SIEM lab (Splunk, Sysmon, centralized logging across Windows/Linux endpoints) plus a Security+ certification and a background in DoD-focused compliance vetting.
What you'll get:
Who this is for: Small businesses or solo IT admins who want real visibility into their network without hiring a full-time security analyst.
Send me the number and OS of machines you want monitored before ordering so I can confirm scope.
Server:
Virtual private server
•
Windows server
Operating system:
Windows
•
Linux
