Browse categories
English
$
USD
Connect to your AI
AWS certified, Azure certified, K8s certified, Terraform certified
I review your Terraform the way a senior engineer joining your team would, and tell you plainly what is solid, what is risky and what to fix first.
WHAT I CHECK
- Module structure and reuse
- State backend, locking and isolation
- Environment separation and drift
- Provider and module version pinning
- Secrets in code and state
- IAM and network exposure created by the code
- The pipeline that runs Terraform (Standard and Premium)
WHAT YOU GET
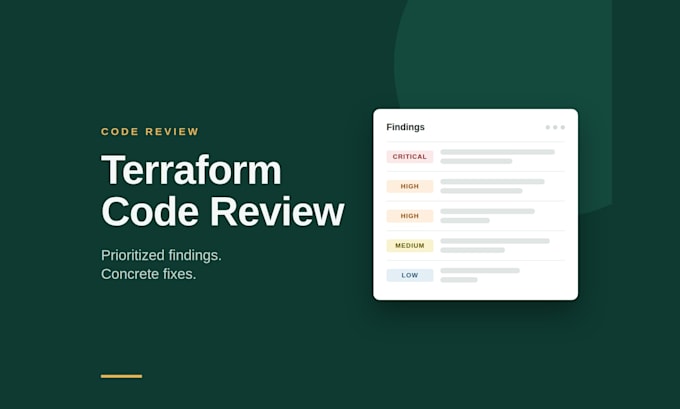
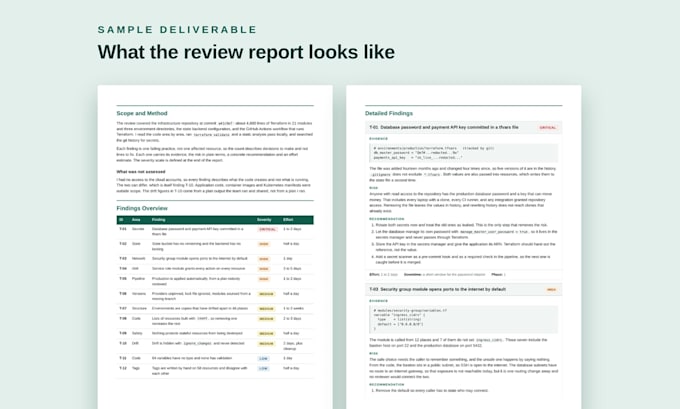
A written report, not a checklist. Every finding has the evidence from your code, the risk in plain terms, a severity and a concrete fix, so your team can use it as a backlog. If something critical turns up, I tell you the same day.
Works with Terraform and OpenTofu, on AWS and Azure, with or without Terragrunt.
Access is read-only. I do not change your code or your infrastructure.
ABOUT ME
My Terraform and Docker courses have 17,000+ students (4.8 rating).
Repository larger than 5,000 lines? Message me before ordering and I will send a custom offer.


Tools:
GitLab
•
GitHub
•
Other
Framework:
Terraform
Programming language:
Other
Expertise:
Configuration
Do you need access to our cloud accounts?
No. This review works from the code and the pipeline configuration. If you also want the running environment assessed, see my AWS assessment gig.
Do you fix the problems you find?
The report tells you exactly what to change and why. Applying the fixes is not included, so your team keeps ownership of the code. I can quote the remediation separately.
Is our code kept confidential?
Yes. I work only inside the access you give me, I do not keep copies after delivery, and I am happy to sign an NDA before we start.
Can I see an example of the report?
Yes. The gallery has a sample report built from a fictional repository, and you can download the full sample PDF there.