Browse categories
English
$
USD
Connect to your AI
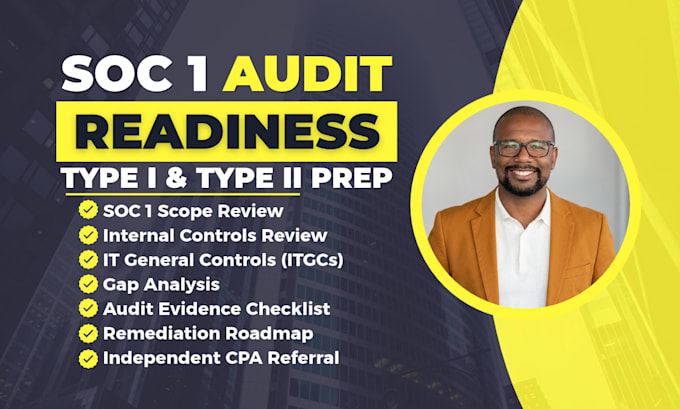
SOC 1 Readiness, US CPA, Tax, Business Compliance
Need SOC 1 audit readiness for a customer, auditor, or vendor due diligence review? I'm an actively licensed U.S. CPA helping payroll processors, outsourced accounting firms, fintech companies, and SaaS providers prepare for SOC 1 Type I and Type II examinations.
I assess controls relevant to your customers' internal control over financial reporting (ICFR), including billing, payroll, transaction processing, reconciliations, and IT general controls (ITGCs), as applicable.
My SOC 1 readiness process:
Choose a SOC 1 scope review, internal controls assessment, or full readiness plan. If you need a signed SOC 1 report, I can recommend an independent CPA firm and help coordinate the handoff.
Message me before ordering with your SOC 1 request, deadline, and systems in scope so I can recommend the right package.
Business type:
Startups
•
SMBs
Industry:
Business services & consulting
•
Cyber security
•
Software
What is included in your SOC 1 audit readiness service?
Basic includes a SOC 1 scope review and starter evidence checklist. Standard includes an internal control gap analysis for up to 10 controls. Premium covers up to 20 controls across two systems and includes a remediation roadmap, audit evidence tracker, and 30-minute walkthrough.
Can you help with SOC 1 Type 1 and Type 2 readiness?
Yes. For SOC 1 Type I, I help you prepare documentation on control design as of a specific date. For SOC 1 Type II, I also help identify what evidence to retain to show how your controls operated over the review period.
What do you check during a SOC 1 gap analysis?
I review your process documentation, control design, control ownership, and available evidence. Depending on scope, this may cover billing, payroll, transaction processing, reconciliations, and IT general controls (ITGCs) such as access management and change management.
Do you offer SOC 1 readiness for SaaS, fintech, and payroll companies?
Yes. I help SaaS providers, fintech companies, payment processors, payroll providers, and outsourced accounting firms assess controls relevant to their customers’ internal control over financial reporting (ICFR).
What’s the difference between SOC 1 and SOC 2?
SOC 1 focuses on controls relevant to your customers’ financial reporting. SOC 2 addresses security and, where applicable, availability, processing integrity, confidentiality, or privacy. If a customer requested a SOC report, share their wording so we can confirm which one they need.
Can I get a signed SOC 1 report through this gig?
The listed packages cover SOC 1 readiness. I’m an actively licensed U.S. CPA and can recommend an independent CPA firm for the SOC 1 Type I or Type II examination and help coordinate the handoff. The examination is scoped and quoted separately.
What do you need to start my SOC 1 readiness assessment?
Share the customer’s SOC 1 request, the requested report type, your deadline, and the systems or business processes involved. If available, include your control matrix, process narratives, or prior SOC 1 report. Message me before ordering so I can recommend the right package.