Browse categories
English
$
USD
Connect to your AI



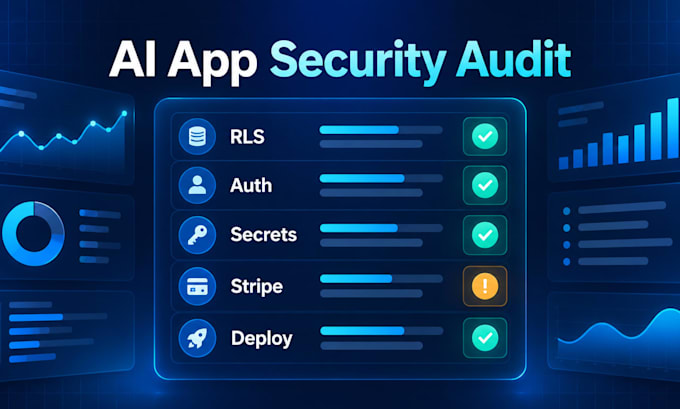
Need a go/no-go before launch? Worried a service-role key or Stripe secret is exposed in the client bundle, RLS allows cross-user data access, or Stripe webhooks are unverified? I review the agreed app scope and rank findings by severity. This is a point-in-time review, not a penetration test. An issue = 1 finding from the agreed list. Basic includes a go/no-go, severity-ranked findings, an anon-key RLS probe, and a secrets-in-bundle check. Standard fixes agreed findings with a verification test; Premium adds storage buckets, edge functions, and one re-test after your deployment. Work is AI-assisted and reviewed by me before delivery. Access is read-only or staging only. Never send production keys in chat; rotate any shared keys after delivery. Complete the required questionnaire and agree the finding list before work starts.
Full Stack and DevOps Developer expert in Claude Code
Languages
How do you handle my secrets and keys?
I work with read-only or staging access only. Never send production keys in chat. Rotate any keys you shared after delivery.
Is this a penetration test?
No. It is a scoped code and configuration review, not a penetration test or a compliance certification.
Do you check Supabase RLS policies?
Yes, for the scope you supply. Runtime behavior still needs validation in your own environment.
Will you deploy the fixes to production?
No. Fixes come in a branch or patch with release and rollback guidance. Your team deploys them.
How many fixes are included?
Each package includes a capped number of agreed fixes: 3 in Standard, 5 in Premium. More work needs a separately agreed scope.
My app is larger than 5,000 lines. Can you help?
Yes. Send the repository size and stack first. I confirm a fitting scope before you order.
How are scope and cancellations handled?
We agree the questionnaire and the finding list before work starts. Each issue is one finding from that list. Cancellations follow Fiverr's order terms.
Do you test live systems?
The RLS probe runs only on staging, or on live systems with your written approval in the questionnaire.
What counts as a finding and a revision?
Each finding is one item on the agreed list. Findings added later need a new order. Revision requests must be sent within Fiverr's 3-day review window; otherwise the order completes automatically.