Browse categories
Explore
Fiverr Pro
English
$
USD
PHP has released an emergency fix for two critical remote code execution flaws known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619, CVSS 9.2). They affect sites running on PHP, including WordPress, WooCommerce, Magento, Drupal and Laravel, and there are already reports of attacks. Older PHP versions that reached end of life may get no fix at all.
Ill make your server safe quickly and without breaking your sites.
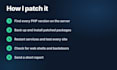
What I do:
Ive been running Linux and hosting servers for 20+ years, including cPanel, Plesk, DirectAdmin and plain servers, and I clean up hacked servers several times a week.
You get a short report: which versions were patched, what was checked and anything that still needs attention.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Linux System Administrator and DevOps Engineer, Security, Migrations
Languages
Will my sites go down during the patch?
Only for a few seconds while PHP services restart. I can do it at a time that suits you, and I check every site right after.
My server runs PHP 7.4 or another old version. Can it be patched?
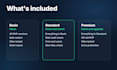
End-of-life versions may not get an official fix. In that case I move your sites to a supported PHP version and test them, or add protection until that’s possible. This is covered by the Premium package.
How do I know if my server was already attacked?
The Standard and Premium packages include a check for web shells, new files, unknown cron jobs and users. If I find anything, I’ll show you and suggest the next steps.
Do you need root access?
Yes, patching PHP needs root or sudo access. When the work is done, I’ll tell you which access to change.


