Browse categories
Explore
Fiverr Pro
English
$
USD

I reverse engineer Android apps to extract their private APIs, then hand you clean, documented Python you actually own - not a black box.
Send me the APK (or a Play Store link) and tell me what you're trying to reach: a feed, prices, account data, or an action the app performs. I capture the app's real traffic, work out the endpoints, auth flow and tokens, and write it all up so your developer can pick it up on day one.
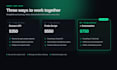
What I can do for you:
I don't hand over the app's source code (I can't - it isn't mine to give). What you get is my own work: the documented API, the scripts and the automation. Those are yours to keep and reuse.
I only take on apps you own or are authorized to test. Message me first and I'll tell you honestly if it's doable, and how I'd approach it.
Android reverse engineering, app security, API reverse and Python automation
Languages
Do you hand over the app's source code?
No - and I can't: the app isn't mine to give. What you get is my own work - the documented API, the Frida scripts and the automation I write for you. Those are 100% yours to keep, reuse and extend.
The API uses tokens or encryption. Can you still do it?
Usually yes. I handle token/OAuth flows, signed requests and SSL-pinning, and I write Frida scripts to bypass root/emulator detection where needed. Send me the APK first and I'll confirm feasibility before you order.
What do you need from me to get started?
Three things: the APK file (or a Play Store link), confirmation you own or are authorized to test the app, and a short note on your goal - which endpoints, data or automation you need. The clearer the goal, the faster I deliver.
Will the automation keep working over time?
APIs change, so I write clean, documented code your dev can update, and I explain how each part works. If the app pushes a big update soon after delivery, message me - I'm happy to help you adapt it. I only build for authorized use.


