Browse categories
English
$
USD
Connect to your AI
Production AI Engineer Agentic AI AWS Azure GCP
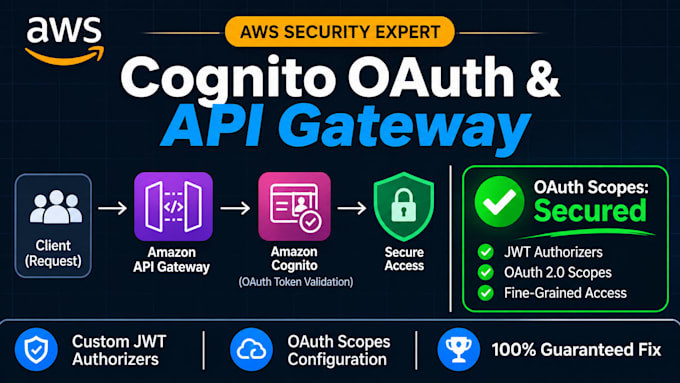
Amazon Cognito oauth scopes and API Gateway authorization configured right. Stop struggling with unauthorized token errors, failing bearer headers, or insecure endpoint routing ruining your cloud backend deployment. I guarantee a permanent, professional solution to your access control roadblocks, ensuring bulletproof application security.
Are misconfigured JWT authorizers, missing permission claims, or broken custom scopes exposing your microservices to security vulnerabilities? Building robust cloud authentication architectures requires specialist engineering, and repeated configuration glitches delay product launches. I eliminate every single technical roadblock by implementing clean security policies tailored to AWS.
What I guarantee to fix and build for you: Integrate Amazon Cognito resource servers with precise OAuth scopes to secure your backend routes Establish robust API Gateway custom authorizers that validate bearer tokens and user roles seamlessly Configure least-privilege IAM policies and CORS headers to prevent unauthorized cross-origin requests Provide end-to-end testing verification along with clear documentation for your engineering team
Cloud Provider:
Amazon Web Services
Frameworks:
Terraform
•
Pulumi
•
Ansible
•
Chef
•
Puppet
What information or access do you need to configure my Cognito OAuth scopes and API Gateway?
Temporary IAM access to your AWS account or your existing Terraform/Serverless configuration files.
Can you integrate custom JWT claims and scopes into my existing API Gateway authorizer?
Yes, I specialize in mapping custom Cognito token claims and OAuth scopes to downstream API routes.
Why are my API Gateway endpoints returning 401 Unauthorized errors with my Cognito tokens?
This usually stems from mismatched issuer URLs, incorrect audience claims, or unconfigured authorizer mappings.
Do you support both REST API and HTTP API gateway configurations in AWS?
I configure secure authorizers and OAuth validation for both API Gateway types.
What kind of documentation do you provide after setting up the authorization pipeline?
You receive a full summary of the architecture, testing instructions, and validation scripts for your client apps.