Browse categories
English
$
USD
Connect to your AI
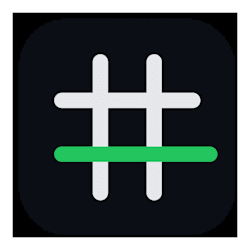

I will do website penetration testing and vulnerability assessment on your web application and send you a clear PDF report your developer can act on the same day.
What I test (manual + automated):
- OWASP Top 10: SQL injection, XSS, CSRF, SSRF, broken access control (IDOR)
- Login, sessions, password reset and user roles
- Security headers, SSL/TLS, exposed files and admin panels
- API endpoints and business-logic flaws
What you get:
- Penetration testing report with every finding verified by hand (no false positives)
- Severity and CVSS score, proof-of-concept screenshots and step-by-step fixes
- A free retest on Standard and Premium, so you know the fixes really work
Why this pentest is different: most VAPT reports are scanner output. Mine explain each issue in plain English, show how an attacker would use it, and give your developer the exact fix.
I only test websites you own or have written permission to test. I do not hack social media, email or any account.
Message me your URL and tech stack before ordering if you are unsure which penetration testing package fits.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Penetration Tester, VAPT, Web App and Vibe Coded App Security
Languages
1. Is this a real penetration test or just a scan?
Both. A scanner finds candidates, then I verify every finding by hand and try to exploit it safely. Anything I cannot prove does not go in the report, so you get no false positives.
2. Will testing break my live website?
No destructive tests are run. I avoid denial-of-service, mass emails and data deletion. If you have a staging copy, I can test that instead of production.
3. What do you need from me to start?
Your website URL, written confirmation that you own it or are allowed to test it, and two test logins if you want user roles tested. Tell me the tech stack if you know it.
4. What is in the report?
A summary for managers, then each finding with severity, CVSS score, affected URL, proof-of-concept screenshots, risk explanation and step-by-step fix. Delivered as a PDF.
5. What does the free retest include?
After your developer fixes the issues, I test the same findings again and send a short retest report showing which are fixed and which are still open.
6. Can you fix the vulnerabilities too?
The report gives exact fixes for your developer. If you want me to apply fixes in your code, message me with access details and I will send a custom offer.
7. Will you hack an Instagram, Facebook or email account?
No. I only do authorised security testing of systems you own. Requests to access other people’s accounts will be refused and reported.