Browse categories
Explore
Fiverr Pro
English
$
USD

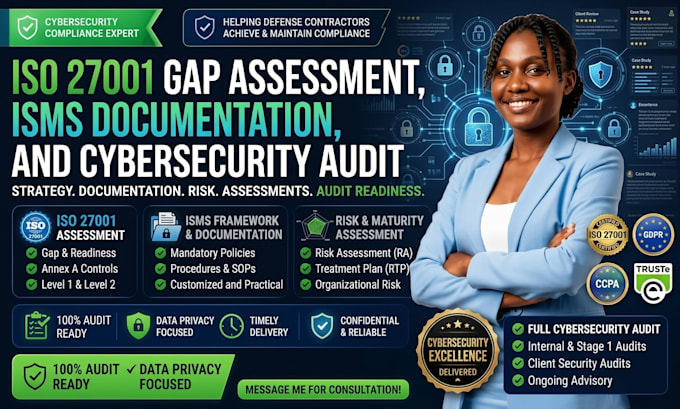
Are you preparing for ISO 27001 certification, needing to pass a client security questionnaire, or looking to strengthen your company's overall cybersecurity stance?
I am Eldora, a cybersecurity consultant and GRC specialist. I help businesses, startups, and organizations establish world-class Information Security Management Systems (ISMS) and achieve audit readiness without operational bottlenecks.
Services Offered in This Gig:
Feel free to send a message before ordering!
CMMC 2 and NIST 800 171 Compliance Consultant GRC DoD Security Expert
Languages
Do you issue official ISO 27001 certificates?
No freelancer or consultant can issue official ISO certificates. Certification must come from an accredited external registrar (Certification Body). I handle all internal prep work, gap assessments, ISMS documentation, and audit readiness so you pass your formal certification audit smoothly.
Can you help if I just need general cybersecurity policies or an information security audit?
Yes! While ISO 27001 provides the core framework, the deliverables (policies, risk management frameworks, and security gap reports) apply directly to overall enterprise cybersecurity and client security requirements.
What information do you need from me to start?
I will need details about your organization size, infrastructure setup (cloud, on-premise, hybrid), current security policies (if any), and key compliance targets.
What is the difference between ISO 27001:2013 and ISO 27001:2022?
The updated 2022 standard restructured Annex A controls into 4 main themes (Organizational, People, Physical, Technological) and introduced 11 new security controls (including Threat Intelligence, Cloud Services Security, and Web Filtering). All assessments and documentation I provide are updated to
How long does the ISO 27001 gap assessment or ISMS drafting process take?
Depending on the package selected, initial gap reports and ISMS documentation frameworks are completed within 3 to 10 business days. For full audit preparation across larger organizations, additional consultation time can be added as needed.
Do you work with cloud-native or remote-first companies?
Yes! I regularly work with cloud-first startups, SaaS companies, and remote teams operating across platforms like AWS, Azure, Google Workspace, and Microsoft 365 to map appropriate security controls to modern cloud environments.