Browse categories
English
$
USD
Connect to your AI
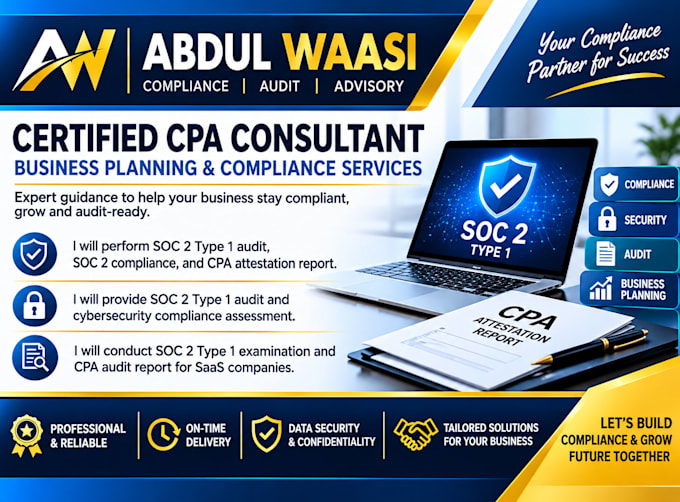

Are you preparing for a SOC 2 Type 1 audit and need professional cybersecurity compliance support? I can help your SaaS company, startup, or growing business strengthen internal controls, identify security gaps, and prepare for SOC 2 compliance.
I specialize in SOC 2 Type 1 audit readiness, cybersecurity compliance assessment, risk assessment, internal control reviews, compliance documentation, and audit preparation support. My goal is to help your organization understand Trust Services Criteria, improve security processes, and prepare for an independent SOC 2 examination.
MY SERVICES INCLUDE:
CPA Consulting Business Planning, SOC 2 Compliance and Audit Readiness for Start
Languages
What is a SOC 2 Type 1 assessment?
A SOC 2 Type 1 examination evaluates the design of relevant controls at a specific point in time against applicable Trust Services Criteria.
Can you help my SaaS company prepare for SOC 2?
Yes. I can help review your current controls, identify gaps, organize documentation, and develop a practical SOC 2 readiness roadmap.
What is included in your cybersecurity compliance assessment?
Depending on the package, it can include control reviews, risk analysis, documentation checks, gap identification, and remediation recommendations.
Do I need existing security policies?
Existing policies are helpful but not always required. I can assess available documentation and identify areas that need development or improvement.
Will you issue an official SOC 2 report?
A formal SOC 2 report must be issued by an appropriately qualified independent service auditor. This gig provides readiness and assessment support unless a separately agreed engagement with a qualified auditor is available.
How long does SOC 2 readiness take?
Timelines depend on your company's size, existing security controls, documentation, and remediation needs. The selected Fiverr package covers only its stated deliverables and timeline.
Can you work with startups and small businesses?
Yes. Services can be tailored to startups, SaaS companies, cloud providers, and small or growing technology businesses based on their needs and scope.
