Browse categories
English
$
USD
Connect to your AI
CI CD, Infrastructure as Code and Cloud Deployments
Infrastructure you can rebuild, review and change safely: clean Terraform modules, separate dev and prod, and security built in from the start.
What you get:
How it works:
AWS work is also available, just message me.
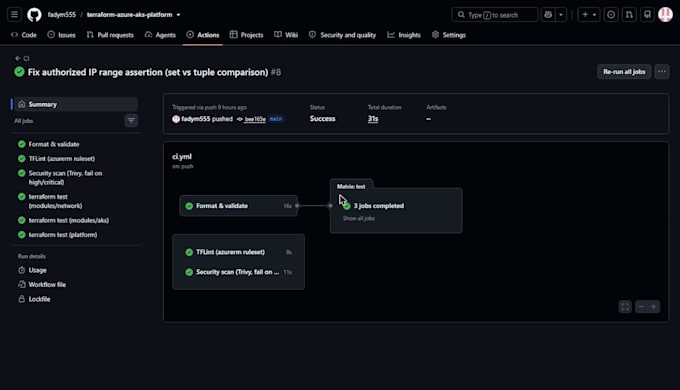
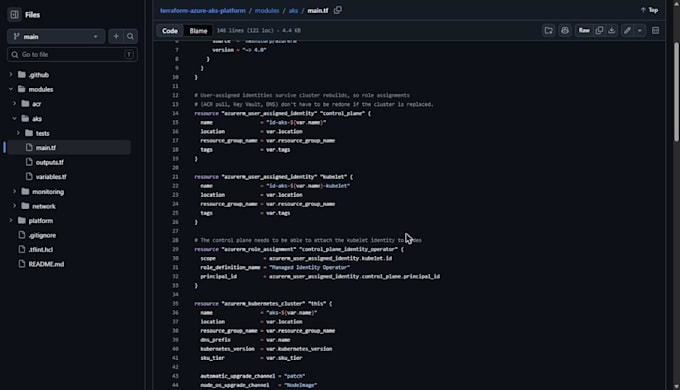
The gallery shows the real CI pipeline for an AKS platform I built, with formatting, lint, security scan and tests all passing.
Not sure which package fits? Message me first and I'll recommend one.
Tools:
Docker
•
GitLab
•
GitHub
•
Azure Resource Manager
•
Hashicorp Vault
Framework:
Terraform
•
Pulumi
•
Ansible
Programming language:
Bash
•
JavaScript
•
Python
•
Golang
•
PowerShell
Expertise:
Migration
•
Development
•
Configuration
Do you need access to my Azure subscription?
Not necessarily. I can write and test the code and hand it over for your team to apply. If you want me to deploy it, a scoped role on one resource group or subscription is enough.