Browse categories
Explore
Fiverr Pro
English
$
USD
Turning messy business processes into clean internal tools
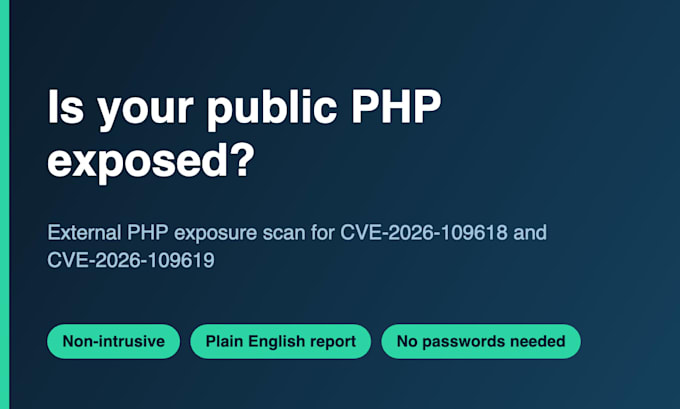
The NCSC has warned that any organisation running PHP may be affected by CVE-2026-109618 and CVE-2026-109619, and says to start with internet-facing systems. This gig finds your public PHP.
What I do:
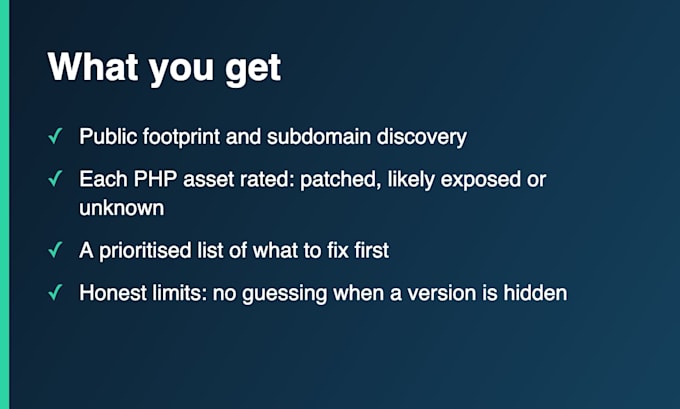
- Discover your public footprint from the domains you give me, including forgotten staging and old marketing sites
- Identify which assets run PHP and, where visible, which version and web server setup
- Compare against the patched releases
- Rate each asset: confirmed patched, likely exposed, or unknown
- Deliver a plain English, prioritised list of what to fix first
This is a non-intrusive scan. I check versions and configuration only. I do not try to exploit the flaw and I will not take your site down.
An honest limit: many servers hide their PHP version, and Linux distributions often patch without changing the version number. Some results will be "unknown" or "confirm on the server", and I will say so rather than guess. My internal inventory gig gives definitive answers.
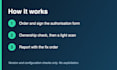
Before I start I need a signed authorisation form and proof you control the domains. This protects both of us. I will send the form after you order. I only test what you own or control.
Server:
Apache HTTP
•
Virtual private server
•
Nginx
Operating system:
Linux
•
Unix
Will the scan take my site down?
It is designed not to. I send light requests, in a window we agree, and I never try to trigger the vulnerability.
Can you scan sites hosted by someone else?
Only the parts you control. Your host's own infrastructure needs the host's permission, so I list those as "ask the provider".
Do you test whether the flaw can be exploited?
No, deliberately. Triggering it risks crashing a live server. I check versions and configuration only.
Why do some results say "unknown"?
Servers often hide their PHP version, and Linux distributions backport fixes without changing it. I report that honestly rather than guess.
Do you need passwords or admin access?
No. The external scan needs only your domains, any IP ranges, and a signed authorisation form.
Do you fix what you find?
Not in this gig. My "update PHP" gig covers patching, and you can order it separately.