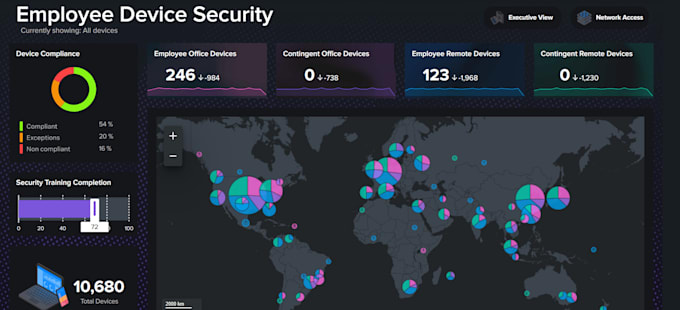
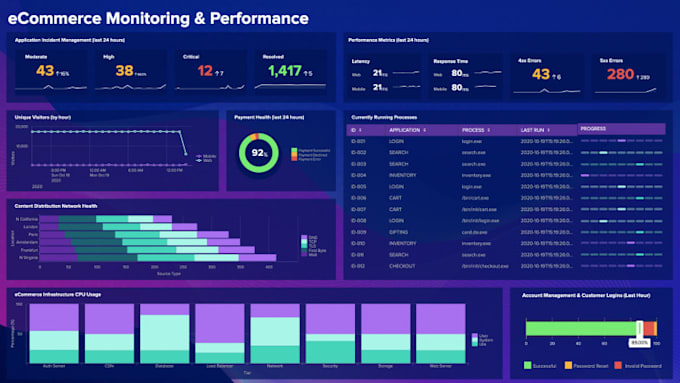
I will build splunk dashboards, spl searches and alerts for your security logs

G
ghislainb742
G
ghislainb742
Ghislain Bukura

About this gig

  • Is your Splunk full of data but short on answers? I'm a Splunk Enterprise Certified Admin and Splunk Core Certified Power User working in a banking SOC. I write SPL every day to catch suspicious logins, malware alerts and network anomalies.
What I can build for you:
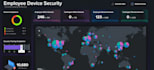
- Security dashboards: failed logins, VPN and firewall traffic, Windows events, Microsoft Defender alerts
- SPL searches written from scratch, or slow ones made fast
- Scheduled alerts and reports that fire on what actually matters
- Field extractions, lookups and basic data onboarding
- Clean Dashboard Studio or Classic XML your team can edit later

How it works:
1. Message me with your goal and Splunk version
2. Share sample events (mask anything sensitive)
3. I build, test and deliver the SPL and dashboard code with notes

I never need admin access to your production Splunk. I work from sample data or a screen share.

Please message me before ordering so we can confirm the scope.

Get to know Ghislain Bukura

Ghislain Bukura

Splunk Admin and SOC Engineer, Splunk Dashboards and Python Automation

  • FromRwanda
  • Member sinceJul 2021
  • Avg. response time2 hours
  • Languages

    English, Kinyarwanda, French, Chinese
Splunk Enterprise Certified Admin and CEH-certified SOC engineer with 3 years in a banking SOC (also Splunk Power User and ISC2 CC). I build Splunk dashboards, SPL searches and alerts, onboard data, write Python and SQL scripts that automate reports and log analysis, and review Microsoft 365, firewall and Windows/Linux security settings. Clear communication in English and French, on-time delivery, and documented work your team can maintain. Message me before ordering and I will tell you honestly if I am the right fit.

My Portfolio