Browse categories
English
$
USD
Connect to your AI
Penetration Tester
I'm a professional bug bounty hunter and pentester. I perform manual and automated security testing to find real vulnerabilities, not just scanner noise.
What I test:
- SQLi, XSS, IDOR, Auth Bypass
- Broken Access Control (OWASP A01)
- API flaws, CSRF, SSRF
- WordPress malware and misconfigs
- Server headers, CORS, CSP
What you get:
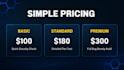
- Full PDF report (Executive + Technical)
- PoC screenshots and curl commands
- Risk rating (Low/Medium/High/Critical)
- Clear remediation steps
Why me:
- Real bug bounty experience
- Reports accepted by HackerOne, Bugcrowd, Intigriti
- Fast response and professional communication
Note: Scope must be in-scope for public bug bounty programs or your own property. No illegal testing.

Testing platform:
Website testing
Device:
PC
•
Linux
Q1: Do you provide proof of concept (PoC)?
A: Yes, every finding includes screenshot, request/response, and curl command. Premium includes screen recording.
Q2: Can you test APIs or mobile backends?
A: Yes. I test REST/GraphQL APIs, JWT flaws, IDOR, rate-limit bypass, and logic bugs with the same depth as web.
Q3: Do you test production websites?
A: Yes, as long as you own the website or have written authorization to test it.