Browse categories
English
$
USD
Connect to your AI
Need to know what an app or binary REALLY does but the source code
is gone, undocumented, or third-party?
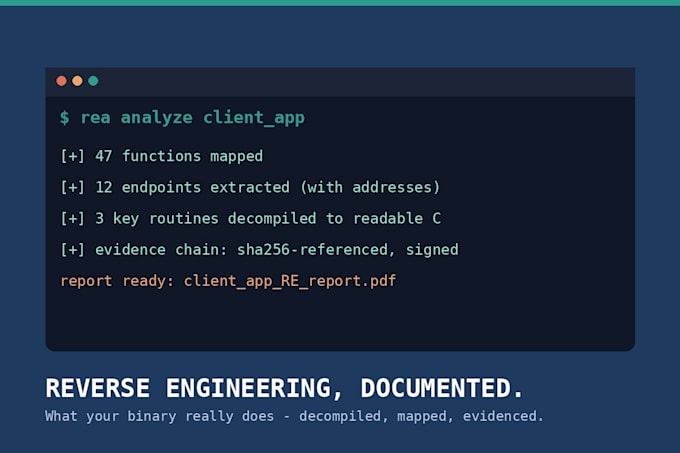
I reverse engineer compiled apps and JavaScript bundles and turn them
into clear, human-readable documentation powered by professional
tooling (Ghidra decompiler + evidence-grade analysis).
WHAT YOU GET (PDF report, evidence-referenced):
Capability map what the app does, module by module
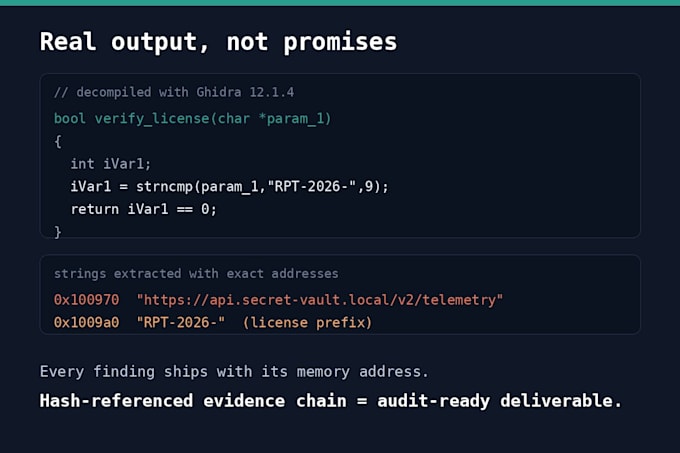
Decompiled logic key functions rebuilt as readable C-style code
Strings & endpoints URLs, config values, hidden data, with exact addresses
Version diff what changed between two builds (Premium)
Evidence chain every finding hash-referenced, ready for your records
USE CASES
Lost your source code? Get the logic back as decompiled pseudocode
Audit a vendor binary before deploying it on your systems
Understand undocumented legacy software you must maintain
Check what data an app sends, and where it connects
WHAT I DON'T DO (please don't order for these):
Cracking, license bypass, DRM removal I decline these orders
Running suspected malware (static analysis only)
iOS dynamic analysis
PRIVACY: your file stays on my own secure hardware, never uploaded
to third-party services, de

Is this legal?
— I only analyze software you own or are authorized to examine: lost source recovery, vendor audits, legacy documentation. I decline any order aimed at bypassing protections.
Can you recover my lost source code exactly?
— You get decompiled C-style pseudocode with all logic intact. Original comments and variable names can't be perfectly recovered from any tool — I add meaningful names where the structure makes them clear.
What formats do you accept?
— Linux/macOS/Windows binaries (ELF, Mach-O, PE), Electron and JavaScript apps, minified bundles (partial). Can you crack or patch software? — No, and I will decline and report these requests.
Is my file safe?
— Analyzed only on my own offline-capable hardware, never uploaded anywhere, deleted on request.